








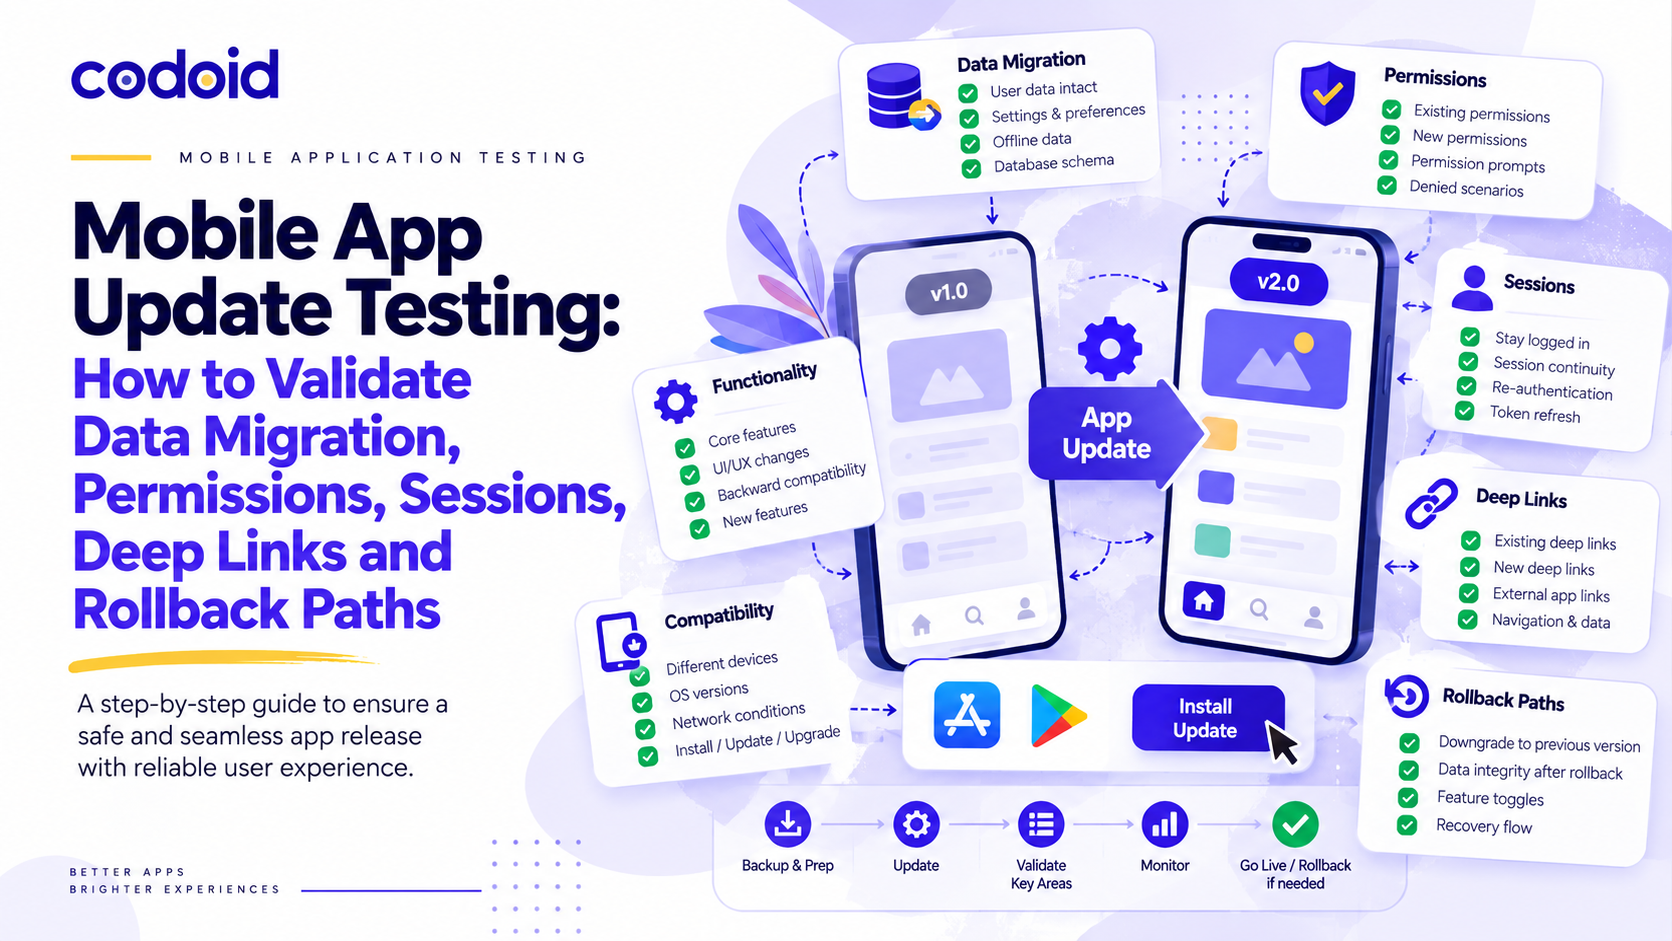
Mobile app update testing verifies that a newer app version works correctly with the data, permissions, credentials, and navigation history left by an older version. A complete test checks the installation, first launch, subsequent use, and failure recovery. It is not simply whether the updated app opens. Fresh-install testing is not a substitute. Apple’s release-testing guidance explicitly identifies data migration, Keychain access, and stored preferences as update conditions that may be absent from a new installation.
The central question is straightforward: can an existing user continue safely after the update, including when something goes wrong? Codoid’s mobile app testing services cover this exact kind of release validation end to end.
Related Blogs
Mobile App Testing Cost: Pricing Guide 2026 | Codoid
How to Choose a Mobile App Testing Company: 15 Questions to Ask Before Hiring a QA Partner
Table of Contents
- What Should Mobile App Update Testing Cover?
- How Do You Prepare a Realistic App Update Test?
- How Do You Validate Data Migration After an Update?
- How Should Permissions Behave After a Mobile App Update?
- How Do You Test Sessions and Secure Storage After an Update?
- How Do You Validate Deep Links After a Mobile App Update?
- How Do You Validate Rollback and Recovery Paths?
- What Should You Automate, and What Should Block Release?
- The Final Standard: Continuity Without Compromising Safety
What Should Mobile App Update Testing Cover?
Use these five areas to organize the test plan and define observable pass criteria. Treat these as acceptance criteria rather than separate smoke tests. For example, opening an old notification after an update may require migration, session restoration, authorization checks, and navigation to succeed together.
| S. No | Test area | What to validate | Evidence of success |
|---|---|---|---|
| 1 | Data migration | Existing records, files, preferences, and pending operations remain usable. | Field-level comparisons, integrity checks, and successful post-update operations. |
| 2 | Permissions | Features respect the current operating-system authorization state. | Correct behavior when access is granted, denied, restricted, or changed. |
| 3 | Sessions | Valid sessions continue where policy allows; invalid sessions fail safely. | Correct account identity, token handling, reauthentication, and logout behavior. |
| 4 | Deep links | Existing links reach the intended authorized destination. | Correct system routing, destination content, parameters, and navigation history. |
| 5 | Rollback and recovery | Failures can be contained and affected installations can recover. | A rehearsed recovery path that preserves required data and security controls. |
How Do You Prepare a Realistic App Update Test?
Start with a genuine older installation, create representative user state, and install the candidate version over it without clearing that state. A structured mobile testing strategy provides the coverage framework this preparation depends on.
Choose Update Paths Based on Installation History
Build the matrix around the versions and data formats your release must support. Include the immediate predecessor, the oldest eligible source version, and releases that introduced significant persistence, authentication, or permission changes.
Test both direct jumps and sequential histories. An illustrative matrix might include 4.8 to 5.2 alongside 4.8 to 5.0 to 5.2. These version numbers are examples. Select actual paths from your installed-base data and support policy.
Record app version, database schema version, operating-system version, and Android target SDK separately. Do not combine an app update and an OS update in every test. First isolate each transition, then test important combinations. The existing mobile app upgrade testing guide covers additional scoping details that complement this approach.
Create Meaningful Pre-Update State
Use the older app to create drafts, saved settings, downloaded files, logged-in accounts, denied permissions, and queued offline operations. Supplement these scenarios with controlled historical database fixtures for edge cases. Behavior around offline and queued operations follows the patterns described in behavior testing for mobile apps.
Capture a baseline of expected record values, attachment identifiers, account identity, permission states, and pending operation IDs. Include empty datasets, large datasets, and unusual but valid text or date values.
Synthetic records created only through the newest model are useful for some tests, but they do not establish that a real older installation updates successfully.
Preserve the Installation During the Update
For a controlled Android APK test:
    adb install app-old.apk

    # Open the old app, create test data, sign in,
    # and set the required permission states.

    adb install -r app-new.apk
The -r option reinstalls the app while retaining its data. Do not insert an uninstall, pm clear, or blanket permission-grant step between the baseline and the update. Those actions change the conditions you are trying to validate.
Use compatible app identity and signing. In particular, distinguish Google Play’s app signing key from the upload key. They can be different. Include store-delivered testing rather than relying exclusively on locally signed builds.
For iOS, exercise the release candidate as an update through TestFlight or the intended distribution method. Test release builds on physical devices, including runs without an attached debugger. Apple notes that debugger behavior can mask watchdog terminations and alter background execution.
How Do You Validate Data Migration After an App Update?
Validate what the data means, not just whether the database opens. Define the expected transformation, compare the resulting records, and prove that interruption or retry does not silently lose or duplicate user work.
Check Records, Relationships, and Usable Files
For each migration, specify which information must remain unchanged and which changes are intentional.
Check identifiers, ownership, relationships, timestamps, text, numeric precision, and default values. A migration that splits one table into two may legitimately change row counts, so “the counts match” is not a sufficient universal rule.
Extend validation beyond the database. Open migrated attachments and downloads. Confirm that preferences still represent the user’s choices. Separate disposable caches from user-created or unsynchronized content before deciding what may safely be rebuilt.
For example, a draft migration should prove that each expected draft retains its content, author, attachment references, and editing capability. Not merely that a “Drafts” screen displays something.
Validate Pending Operations Before and After Synchronization
Seed offline edits and queued uploads in the old version. After updating, inspect them before reconnecting.
Then restore connectivity and verify that pending operations reach the correct account and resource, retain their intended ordering where required, and do not produce duplicate business actions.
Use stable operation identifiers to compare the local queue with server outcomes. Do not treat a successful network response as sufficient evidence that the correct operation was applied.
Use Migration Helpers Without Mistaking Them for Complete Validation
For Android Room, retain exported historical schemas and use MigrationTestHelper to exercise migration paths. Room’s documentation explicitly distinguishes schema validation from data validation. The helper verifies schema changes, but tests must separately check that data migrated correctly.
For SQLite-backed stores, PRAGMA integrity_check can detect structural and consistency problems. Foreign-key violations require PRAGMA foreign_key_check. Neither check proves that a transformed value is correct for your business rules.
Interrupt the Migration Deliberately
Run controlled failures before transformation, during processing, and around durable checkpoints. Exercise low storage, unavailable files, process termination, and repeated launches.
Require a defined outcome: safe completion, safe retry, or a recoverable error that preserves the original information. Make retry behavior idempotent. Repeating a completed step must not duplicate its effects.
For changes spanning databases, files, and preferences, test recovery across all stores. Do not accept a database transaction as evidence that separate file operations are also recoverable.
Finally, test entry points that might compete with initialization, such as notification handling or background work. For patterns on handling these lifecycle interruptions, refer to interruption testing in mobile applications.
Do not hide migration defects with destructive fallback. Room documents that destructive migration fallback can permanently delete table data when a migration path is missing. That may be acceptable for an explicitly disposable cache, but it is not a safe default for user-created content.
How Should Permissions Behave After a Mobile App Update?
The updated app should follow the operating system’s current authorization state, not a saved assumption that permission was granted previously. Android’s guidance requires checking permission whenever performing an operation that needs it and handling denial or revocation gracefully.
Test More Than Allow and Deny
Create separate pre-update cases for previously granted access, previously denied access, and permissions changed in system settings.
After updating, invoke the actual protected feature. A permission screen that looks correct is not enough. Attempt the camera capture, microphone use, or other relevant operation and verify both successful access and safe refusal.
Where the platform supports them, include temporary and partial authorization. Android supports one-time grants for certain permissions and mechanisms that reset unused permissions. Do not treat these as permanent grants.
On iOS, limited Photos access is a distinct state. Test access to the selected assets and verify the experience when an asset is outside the authorized selection, rather than assuming all-or-nothing library access. Runtime permission handling for automation is covered in the Patrol framework for enterprise Flutter testing.
Separate App Updates from OS Permission Transitions
Android notification permission illustrates why this distinction matters. When a device upgrades to Android 13 or higher, eligible existing apps can receive an automatic notification permission pre-grant. Eligibility includes an existing notification channel and the absence of a prior user-disabled notification state. This is not a blanket rule that every app update grants notification access.
Test relevant target-SDK transitions separately from ordinary app-version changes.
For newly introduced permission-dependent features, verify the timing and explanation of the request, the cancellation path, and continued access to unrelated functionality. Android recommends requesting permissions in context and degrading gracefully when access is denied.
Keep OS authorization separate from application preferences and consent settings. Your test should check each independently rather than using one as a substitute for the other.
How Do You Test Sessions and Secure Storage After an Update?
Preserve sessions that remain valid under the application’s security policy, and require reauthentication when continued access is no longer valid. Avoid defining success as “every user stays logged in.”
Exercise Valid, Expired, and Revoked Credentials
Create cases for a valid session, an expired access token with a usable refresh token, an expired or revoked refresh token, and a user who explicitly logged out before updating. Security testing for these token scenarios is detailed in the OWASP Mobile Security Testing Checklist.
OAuth’s security guidance recognizes refresh-token expiration, revocation, and rotation. Therefore, credential presence alone is not evidence that a session remains authorized.
For each case, verify the result at both the interface and server:
- A valid continuation should use the correct account and permissions.
- A failed continuation should show a controlled sign-in path rather than a retry loop.
- A logged-out user should not regain a session because an old local flag or cached screen survived.
Add account-switching tests. Confirm that cached content, queued operations, and restored navigation remain associated with the intended account.
The backend must enforce authentication and authorization. A protected-looking mobile screen is not the security boundary. OWASP MASVS makes remote enforcement explicit.
Stress Refresh and Retry Behavior
Trigger several authenticated requests immediately after the update, including a case where the access token expires at first launch.
Where refresh-token rotation is used, test coordination between requests and durable storage of the replacement credential. RFC 9700 describes rotation as issuing a new refresh token and invalidating the previous one, making stale-token reuse a meaningful failure case.
Also interrupt the app during refresh. Define when safe recovery requires reauthentication instead of repeatedly retrying credentials that may no longer be valid.
Test offline launch separately. Specify which cached content may remain accessible and ensure that a connectivity failure does not automatically become an invalid-credentials conclusion.
Read Credentials Created by the Old Version
On iOS, compare release entitlements and Keychain access groups, then attempt to read items written by the previous app. Apple documents that Keychain access depends on access-group membership, so testing only newly created credentials misses an important update condition.
Apply the same historical-data principle whenever encrypted storage formats, key aliases, or credential-storage libraries change. Include successful legacy reads and a controlled recovery path for unavailable credentials.
How Do You Validate Deep Links After a Mobile App Update?
Test both layers: whether the operating system routes the link correctly and whether the app reaches the intended authorized content. “The app opened” is only an intermediate result.
Verify the App-to-Domain Association
For Android App Links, inspect the device’s verification state and confirm the release configuration matches the intended domains. Android App Links provides commands to inspect and re-run domain verification.
For example, on a supported Android test device:
adb shell pm get-app-links --user cur com.example.app
Use this to inspect the existing state before changing it. Keep reset-and-reverification tests separate from tests of the state naturally inherited during an update.
For iOS Universal Links, verify both the website’s apple-app-site-association configuration and the app’s associated-domains entitlement. Apple defines these as the two sides of the app-to-website trust relationship.
Test Historical Links Through Real Entry Points
Maintain a set of links from previous releases: saved content links, email links, notification destinations, invitation links, and supported custom-scheme routes.
Open them from representative sources instead of exclusively invoking an internal navigation function. A test that forces a specific app component does not establish that normal system routing works.
For each supported link, assert the destination screen, resource identifier, relevant parameters, account context, and back-navigation behavior. Include renamed routes, unavailable content, malformed parameters, and unsupported paths.
Check the documented fallback when the app is not installed, while keeping that scenario separate from update testing.
Cover First Launch, Authentication, and Repeated Delivery
Make an old link the first entry into the updated app. Verify that routing waits for any required migration and session initialization rather than reading partially prepared state.
Repeat link tests after the app has launched successfully, both while it is running and after termination.
When login is required, retain the intended destination and validate it again after authentication. Test cancellation, switching accounts, and receiving the same link more than once.
A link must not bypass resource authorization. Verify server-side access checks even when the route and resource identifier are valid.
How Do You Validate Rollback and Recovery Paths?
Test recovery on installations that have not migrated, have partially migrated, and have completed migration. Treat stopping distribution, disabling a feature, restoring data, and replacing the installed binary as different operations.
Understand What Rollout Controls Actually Do
On Google Play, halting a staged rollout prevents additional users from receiving that version, but users who already received it remain on it.
Google Play also supports halting eligible fully rolled-out releases, allowing a previous eligible release to become available to users who are not on the halted version. This should not be treated as reversing migrations on already-updated devices.
Apple’s phased release controls automatic distribution. Users can still manually download a phased update, so pausing the phase is not equivalent to making the update unavailable or repairing affected installations.
Rehearse the Recovery Mechanism You Actually Have
| S. No | Recovery mechanism | What the test must prove |
|---|---|---|
| 1 | Feature disablement | The app can reach the control, apply it safely, and behave acceptably with cached or unavailable configuration. |
| 2 | Backend reversion | Both older and updated clients still receive compatible responses and can submit valid operations. |
| 3 | Local checkpoint or backup restoration | Restoration produces consistent state and accounts for user changes made after the checkpoint. |
| 4 | Forward-fix release | The fix handles untouched, fully migrated, and partially migrated installations without requiring a reset. |
| 5 | Binary downgrade, where supported | The actual distribution method allows it, and the older code can safely handle the resulting local state. |
A lab downgrade is not sufficient evidence of a production recovery path. Test the delivery mechanism and the data compatibility, not just whether a tool can install an older package.
Protect Writes Created After the Update
Suppose an update migrates a store successfully and the user then creates several offline drafts. Restoring a pre-update snapshot without reconciling those drafts would discard them.
Include that sequence in recovery testing. Establish which changes must survive, how they will be retained or replayed, and how conflicts will be resolved.
Also test a crash that happens before remote configuration loads. A remote feature switch is useful only if the affected installation can reach the code that reads and applies it.
Document the recovery trigger, responsible owner, compatible versions, verification steps, and acceptable data-loss policy. “Ask the user to reinstall” should not count as successful recovery when required local work would be lost.
The release readiness framework in the mobile app launch checklist provides go/no-go criteria that apply directly to update releases, including rollback readiness and defect thresholds.
Related Blogs
Mobile App Launch Checklist: A Release Readiness Guide for QA Teams
Mobile App Analytics Testing: A Practical Guide for Developers and QA Teams
What Should You Automate, and What Should Block Release?
Automate state preservation and outcome checks, not merely installation commands.
Use persistence-level tests for historical fixtures and transformation rules. Add device-level tests that install an old build, create state, update in place, and inspect the result. Finally, exercise complete user journeys against the appropriate backend configuration.
Audit the test harness itself. Confirm that setup hooks are not uninstalling the app, clearing storage, resetting permissions, or signing in again before assertions run.
An illustrative end-to-end case is to create an offline draft in an older version, deny a relevant permission, save a legacy content link, and then update. Check the draft before synchronization, open the saved link, validate account identity, and complete the pending operation after reconnecting. Repeat from the same baseline in separate interruption and recovery runs.
A practical release gate should require:
| S. No | Gate | Requirement |
|---|---|---|
| 1 | Correctness | No known unexplained loss, duplication, account crossover, or permission bypass in the required update paths. |
| 2 | Recoverability | The selected recovery mechanisms have been exercised against realistic post-update state. |
| 3 | Observability | Failures can be identified by source version, target version, schema, OS, and relevant configuration. |
Track migration starts, completions, failures, and unresolved attempts. Monitor first-launch failures, unexpected reauthentication, link-to-destination failures, and recovery outcomes. Do not count missing completion events as success.
Set performance thresholds against your application’s baseline and supported devices rather than adopting an arbitrary universal number. Performance validation patterns for mobile releases are covered in Android and iOS quality assurance.
Keep diagnostic evidence free of passwords, tokens, and sensitive payloads. OWASP specifically identifies logs and backups as possible sources of unintended sensitive-data exposure.
For teams that need expert support building this layer, Codoid’s QA automation services integrate update testing into release pipelines.
The Final Standard: Continuity Without Compromising Safety
A mobile app update should preserve more than the ability to launch. It should preserve the user’s work, respect current access decisions, maintain the correct identity, and honor existing navigation paths. Approve the release only when those outcomes, and the recovery path when they fail, have been demonstrated on realistic existing installations.
Need Help Testing Your Mobile App Updates?
Talk to a Mobile Testing ExpertFrequently Asked Questions
-
Is update testing the same as regression testing?
No. Regression testing checks whether existing behavior still works. Update testing adds a specific transition: new code must handle state created by an older installation. Fresh-install regression tests do not reproduce that history. Apple recommends testing the update scenario when a release must support prior app data.
-
How many previous app versions should be tested?
Base coverage on eligible source versions, active installation history, and distinct data formats. Prioritize the immediate predecessor, the oldest supported path, and versions crossing significant migration or authentication changes. Testing only the last two releases should be a justified decision, not an automatic rule.
-
Is backup-and-restore testing the same as an in-place update?
No. Treat it as a separate scenario. Android documents restoration during installation, including device setup and supported reinstall flows. That can introduce historical data through a different path from updating an existing installation. Test the restored state explicitly.
-
Does stopping a rollout fix users who already updated?
No. Google Play explicitly states that users who already received a halted staged release remain on that version. Affected installations need a separate mitigation or recovery path, such as compatible server behavior, feature disablement, or a tested corrective release.
-
Why can fresh-install testing not replace update testing?
A fresh installation has no prior data, no stored credentials, no historical permissions, and no navigation history. Update testing specifically validates how new code handles the state left behind by an older version. Apple's release-testing guidance identifies data migration, Keychain access, and stored preferences as conditions that only appear during an update, which is why fresh-install regression suites miss them entirely.
-
What should I test first when planning an update test cycle?
Start with data migration for the immediate predecessor version. Data loss is the most damaging and least reversible failure mode. Once migration is verified, move to permissions, sessions, deep links, and finally rollback and recovery paths. This order reflects the severity of impact if something fails in production.
-
How do I test permission changes after an app update?
Create separate pre-update test cases for previously granted access, previously denied access, and permissions modified in system settings. After updating, invoke the actual protected feature, not just the permission prompt. Verify both successful access and safe refusal. Where the platform supports it, include temporary and partial authorization states, since Android one-time grants and iOS limited Photos access are distinct from permanent approval.
-
How do I test sessions after a mobile app update?
Build separate cases for a valid session, an expired access token with a usable refresh token, an expired or revoked refresh token, and a user who explicitly logged out before updating. Credential presence alone is not evidence that a session remains authorized. Verify the result at both the interface and the server. A valid continuation should use the correct account, a failed continuation should show a controlled sign-in path, and a logged-out user should not regain a session from a stale local flag.
-







Comments(0)