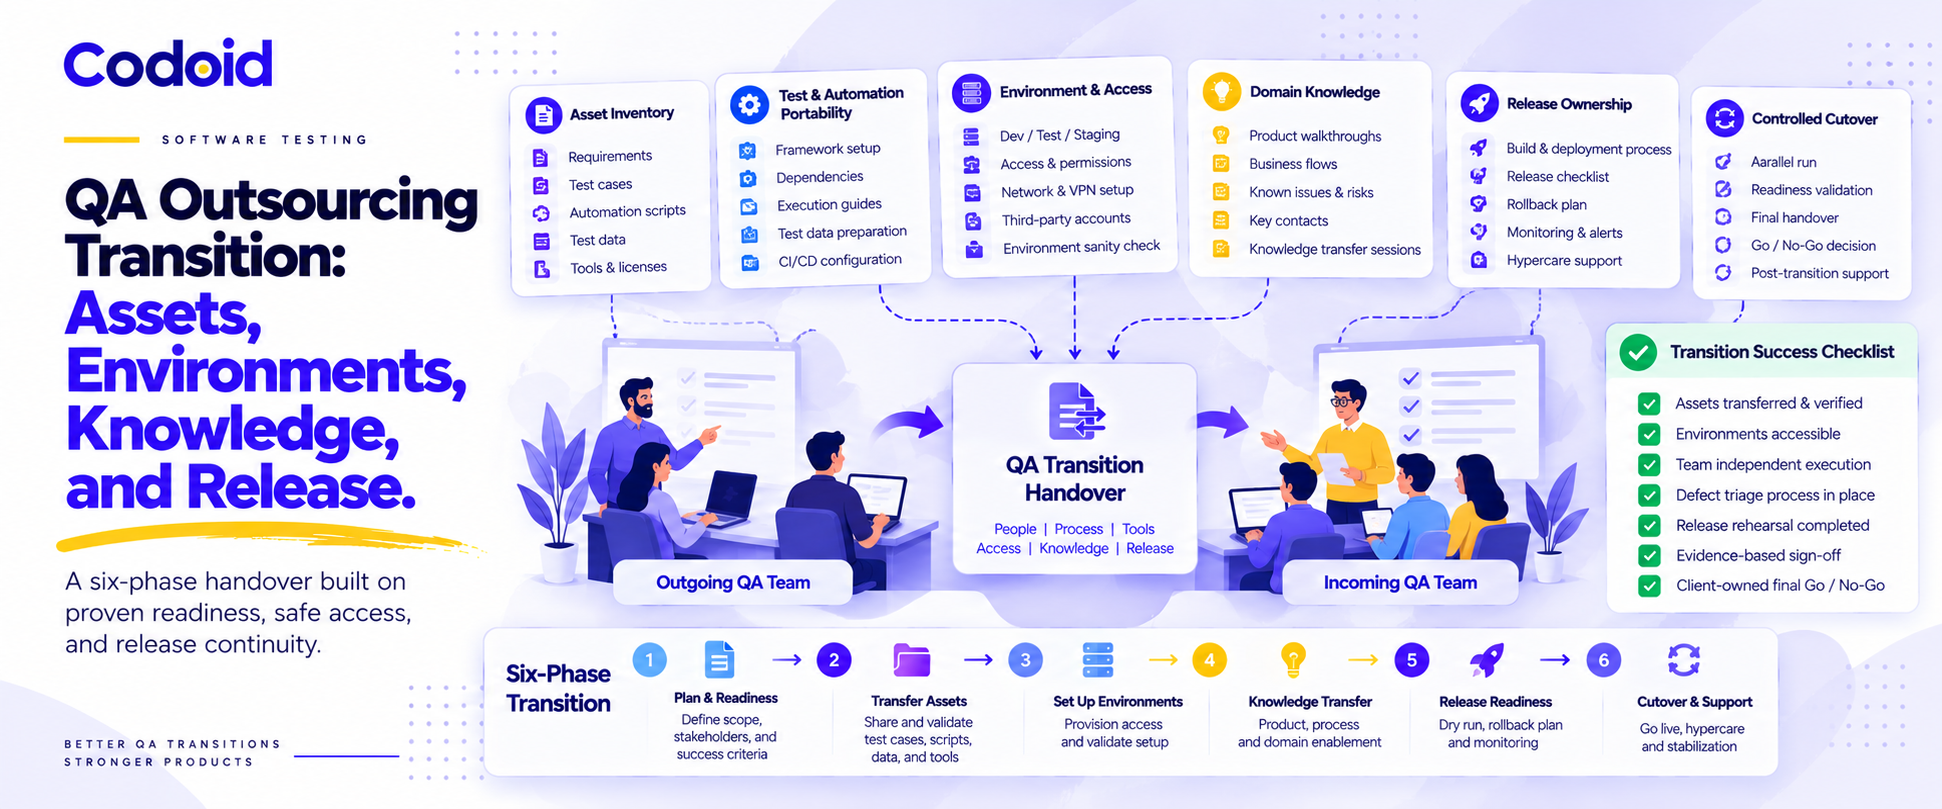
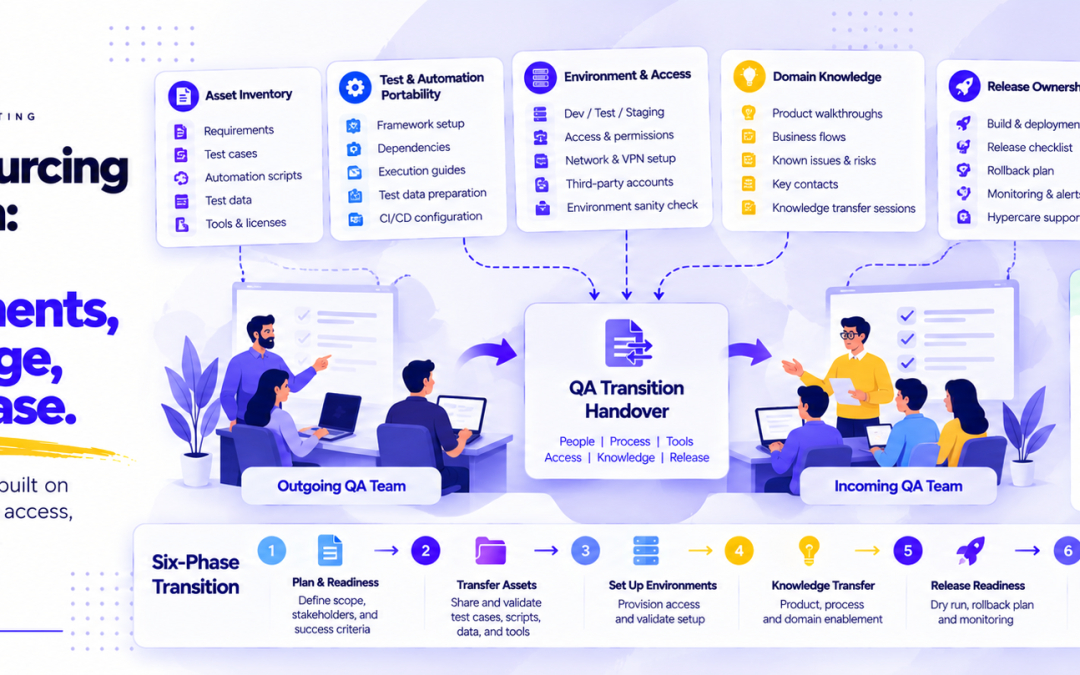
To transition QA to an outsourcing partner without creating release gaps, define the responsibility boundary, inventory and transfer the testing estate, and then verify the incoming team’s capability through independent execution, defect triage, environment recovery, and release rehearsals. Approve cutover only when the evidence meets agreed criteria and the client has a workable fallback. This guide is for QA and engineering leaders taking their first step into outsourced testing or replacing an existing QA supplier. Use the six phases in order, then copy the working checklist into your transition tracker. A test repository, a training attendance record, or a successful smoke test is not sufficient proof that the new team can operate independently. A disciplined QA outsourcing transition is a tested change to your operating model, not a file transfer.
At a glance: define accountable owners, baseline assets and risk, prove test and automation portability, provision environments and access safely, validate domain expertise, and rehearse QA readiness and release gates before removing outgoing-team access.
A QA Transition Succeeds Only When the Incoming Team Can Operate Independently
Transition completion means demonstrated capability, not delivery of files. The incoming team should be able to select risk-based coverage, prepare test data, execute and maintain tests, investigate failures, submit useful defects, report residual risk, and operate only those release gates expressly delegated to it. The client must still name the person authorized to accept business risk and issue the final go or no-go decision.
ISO 37500:2014 describes outsourcing as an arrangement with governance, risk management, and responsibilities that may differ by phase and by client-provider relationship. Its public abstract is general outsourcing guidance rather than a QA-specific certification requirement (Source: ISO 37500).
A useful supporting analogy is Google’s SRE onboarding model. Teams train through hands-on exercises, assume duties progressively, transfer access and change-management responsibilities, and retain temporary backup from the previous owners. That model is about production operations, not a prescriptive QA outsourcing standard, but it supports an evidence-led cutover.
For every transferred capability, capture the receiving owner, the test of independence, the evidence location, the evaluator, and the client approver. Treat a failed exercise as a tracked transition defect, not as an informal follow-up.
Define the Ownership Boundary Before Transferring Anything
Decide what the external QA team will perform, what internal engineering, DevOps, and security teams will retain, and which decisions cannot be delegated without explicit authority. Record the scope in a responsibility assignment matrix before accounts, repositories, or tickets change hands.
Build a Responsibility Matrix for QA Operations
In the example below, R means responsible for performing the activity. A means accountable for the decision or outcome. This is an illustrative allocation, not a universal contract model.
S. No
Activity
Incoming QA partner
Client-side accountable owner
Evidence of ownership
1
Test strategy and prioritization
R: proposes risk-based plan
A: QA lead or product owner
Approved plan for next release
2
Manual and automated execution
R: performs tests and retains results
A: client QA lead for agreed scope
Independent runs and reviewed reports
3
Automation maintenance
R: fixes and extends agreed suites
A: designated repository owner
Reviewed change through CI
4
Test-data preparation
R: uses approved synthetic or authorized data
A: data owner or security
Logged preparation and cleanup drill
5
Environment diagnosis and recovery
R: first-line diagnosis within permission boundary
A: internal DevOps or platform owner if retained
Approved recovery exercise
6
Defect triage
R: reproduction and impact evidence
A: product or engineering for business priority
Representative triage record
7
QA release-readiness recommendation
R: supplies evidence and recommendation
A: client QA or release governance owner
Accepted readiness report
8
Final production go or no-go
C: provides risk advice, not automatically approver
A and R: named client business or engineering approver
Decision and exception record
The contract and operating model may place additional responsibilities with the provider, but vendor QA approval must not silently become business release authorization. Also name backup approvers, an emergency escalation path, and the team that owns change control.
For a vendor replacement, verify the signed arrangements governing test-code and report ownership, intellectual-property rights, repository and account custody, licenses, confidentiality, exit assistance, permitted subcontractors, retention, and data return or deletion. Legal and privacy specialists should interpret these obligations. A blog checklist is not legal advice. The contract review is a conditional gate, not an assertion that every jurisdiction imposes identical terms.
Define Transition Acceptance Criteria
Make each phase pass an exit gate before its dependent responsibilities move. The client transition owner decides whether remaining gaps are tolerable, and the risk owner documents each exception.
S. No
Phase
Minimum exit demonstration
Accountable evaluator
1
Baseline
Reconciled risk-ranked register, known gaps, and ownership
Client QA lead
2
Assets
Clean checkout, CI execution, triage, and maintenance change
QA automation lead
3
Environment and access
Approved task-based access, safe data use, recovery escalation
Security and platform owners
4
Domain
Critical journey teach-back and defect investigation
Product or domain owner
5
Release gates
QA recommendation and blocked-release rehearsal
Client release manager
6
Cutover
Incoming-led representative cycle and agreed fallback
Client transition sponsor
These are example gate categories, not numerical thresholds. Define the required journeys, integrations, platforms, permissible exceptions, and number of rehearsals for the specific product. High-risk changes may need more than one representative cycle.
Phase 1: Inventory the Existing QA Estate and Establish a Baseline
Create a Test-Asset Register
Inventory active manual suites, exploratory charters, automation repositories and dependencies, shared utilities, test-data generators, API collections, CI jobs and runners, test environments, device and browser matrices, defect backlogs, reports, dashboards, traceability, and retained evidence. Mark obsolete suites for archive or retirement after checking whether they contain unique coverage. Do not migrate everything merely because it exists.
S. No
Asset
Custodian or destination
Dependency and risk
Required transfer proof
1
Critical regression cases
Client test-management workspace
Shared steps, tags, requirement links
Count and relationship reconciliation
2
Automation repository
Client-controlled or contractually agreed Git host
Runtime, lockfile, runner, service licenses
Independent build, run, and maintenance PR
3
Test-data builder
Approved repository or data owner
Seed data, cleanup, sensitive fields
Reproducible creation and reset
4
Results and defect history
Client-controlled report or archive
Attachments, run IDs, and retention
Sample historic report retrievable
5
Web accessibility test assets, if in scope
Agreed test-management location
Applicable WCAG target, assistive technology, and browser matrix
Manual and automated evidence to agreed scope
If accessibility testing is part of the mandate, specify the target, such as WCAG 2.2 Level AA where applicable and contractually chosen, together with assistive-technology and browser combinations. Automated scans alone cannot establish full conformance. W3C describes WCAG evaluation as involving automated checks and human evaluation (Source: W3C WCAG overview and W3C conformance explanation).
Inventory Environments and Dependencies
For each QA or staging environment, record its owning team, build and deployment paths, API endpoints and third-party sandboxes, feature flags, identity provider, database and queue dependencies, supported devices, certificates, secrets-management references, CI agents, logs, dashboard access, data refresh or reset procedures, shared usage windows, and incident escalation route. Record permissions needed for specific operations, not merely URLs.
Record the Current Operating Baseline
Before any transfer, capture required critical journeys, current coverage gaps, release blockers, flaky or quarantined tests, open defects, exceptions, data restrictions, and typical build and release cadence. If the organization uses metrics, agree a small dictionary instead of comparing raw vendor dashboard numbers.
S. No
Metric
Definition and caution
Baseline owner or source
1
Required test execution coverage
Executed eligible planned tests divided by all eligible planned tests. Report blocked and not-run separately
QA lead or test management
2
Critical journey evidence
Named required journeys with accepted evidence divided by required journeys. Any omitted journey must be explicit
Product owner or coverage map
3
Automation instability
Identified nondeterministic failures over a stated time window. Separate app failures, reruns, and quarantines
Automation owner or CI
4
Defect triage turnaround
Time from valid report to first agreed triage decision. Compare like-for-like severity and time windows
Defect lead or issue tracker
A pass-rate percentage alone can hide unexecuted high-risk tests. Always show its numerator, denominator, exclusions, blocked cases, and unresolved material defects. Do not imply that a universal percentage makes a release safe.
Phase 2: Transfer Test Assets Without Losing History or Dependencies
Move Manual Test Assets With Traceability Intact
Migrate the approved active cases together with suite hierarchy, shared steps, parameters, configuration, expected results, links, attachments, ownership, and appropriate historic evidence. Check counts and relationships, then sample critical workflows end to end. Archive retired or obsolete cases where agreed instead of treating archive size as coverage.
Transfer Automation as Maintainable Source Code
Handover must include the source repository and permissions, language and runtime versions, dependency manifests and lockfiles, CI configuration and runner ownership, service accounts, schedules, test-data fixtures, report publication, failure artifacts, licensing, supported browsers and devices, known flaky or quarantined cases, and procedures to create, run, debug, and modify tests. Check third-party provider-hosted runners and service tokens. A repository is not independent if the new team cannot execute it after the outgoing vendor leaves.
Codoid’s public guide on QA automation services also emphasizes framework maintainability, CI gating, and a genuine handover rather than a list of tools.
Reconcile What Migration Tooling Does Not Preserve
Do not infer migration completeness from a success message. Microsoft documents that Azure Test Plans copy and import operations can preserve test-suite hierarchy and configurations while not preserving test run history, results, or tester assignments. Preservation of shared parameters and links also depends on the operation. Check the actual capabilities of the tool and migration path used.
For each category, record source count, destination count, preserved relationships, deliberately excluded assets, separately archived evidence, sampling result, and unresolved mismatch. If historical runs cannot move, retain the required records in an approved and searchable archive with an owner and retention rule.
Prove Portability With an Independent-Operation Test
Use a receiving-team engineer who was not the outgoing suite’s primary author. The evaluation should cover both a successful run and a controlled failure.
Preconditions: named repository and CI roles are approved. A non-production environment is available. Permitted synthetic test data exists. Runner dependencies and reporting destination are documented.
Actions:
Perform a clean checkout.
Install locked dependencies.
Configure through approved secrets references.
Create or reset synthetic data.
Run a risk-selected suite through CI.
Diagnose a deliberately broken non-production assertion.
Fix or explain the failure.
Submit an automation change for normal review.
Publish an evidence-linked report.
Pass criteria: no undocumented outgoing-vendor access. Expected critical tests execute or have a signed exception. A controlled failure is correctly detected and triaged. A maintenance change passes approved review. Log and report access works for the new owner. Failing one mandatory criterion means Fail, even if overall test counts look high.
S. No
Field
Example entry
1
Scenario and owner
AT-02 and Incoming automation lead
2
Required behavior
Run checkout tests from client-controlled CI. Seed and clean test data. Diagnose a broken test and publish a report
3
Observed issue
Example: runner requires a token owned by the outgoing supplier
4
Expected result and evaluation
Fail until approved replacement identity works and the full exercise is rerun
5
Evidence
Placeholder: CI-RUN-EXAMPLE, PR-EXAMPLE, redacted triage log, not live links
6
Exception and risk owner
No bypass approved. Client DevOps owner assigned token migration
7
Evaluator and approver
Client QA automation lead and client transition sponsor
8
Sign-off timestamp and status
Not signed. Fail in this hypothetical record. Populate actual date and time only after witnessed retest
This record illustrates why an apparently green smoke run must not override a hidden ownership dependency.
Phase 3: Transfer Environments, Integrations, and Access Safely
Document Environment Topology, Not Just URLs
Capture component versions, integration topology, deployment paths, allowed reset or rollback operations, data dependencies, alerting and logging, change windows, shared-user impact, and recovery contacts. A dangerous database reset or queue purge must not be carried out solely to prove a handover. First confirm non-production scope, permitted operator, change approval, backup and rollback prerequisites, and escalation to platform or DevOps owners.
Re-Provision Credentials Instead of Handing Around Secret Values
Provision named accounts and appropriately scoped service identities instead of transferring passwords. Use the organization’s approved identity provider, multifactor authentication, least privilege, session and audit logging, and time-bounded access reviews. NIST SP 800-53 Rev. 5 provides a customizable security and privacy controls catalog covering access control, identity and authentication, and audit. It is not a blanket statement that every QA supplier must implement every control.
S. No
Access record field
Purpose
1
System
Identifies the target environment or service
2
Incoming identity
Named account or service principal
3
Business justification
Documents why access is required
4
Requested role or permission
Scoped privilege level
5
Data classification
Defines handling requirements
6
Authorizing owner
Named approver
7
Multifactor authentication requirement
Confirms MFA is enforced
8
Provisioned date
Start of access window
9
Review or expiry date
Forces periodic recertification
10
Logging or audit location
Where activity is recorded
11
Revocation owner
Who removes access
12
Verification evidence
Proof that access was tested
Verify approved remote-work locations, devices, and subcontractor access where applicable.
Data and evidence safeguards: Prefer synthetic or minimized test data. When production-derived or pseudonymized data is necessary, obtain explicit data-owner and privacy approval, enforce applicable masking and transfer controls, and specify access purpose, location, retention, and destruction. Pseudonymized records may still be personal data under relevant laws. Where UK GDPR controller and processor requirements apply, the ICO describes mandatory contractual terms including authorized processing, security, subprocessors, and deletion or return at contract end. Do not generalize that legal regime to every QA engagement.
Defect attachments, logs, screenshots, and API traces should use approved storage and restricted access. Capture minimum necessary data, redact tokens, passwords, connection strings, and personal or regulated information, and establish retention and deletion rules. The OWASP Logging Cheat Sheet explicitly identifies these categories as data that should generally be excluded or protected in logs.
Validate Access Through Tasks
Have the incoming team demonstrate its authorized work. Clone code. View CI artifacts. Launch a permitted test job. Read an approved log. Seed data. Access agreed dashboards. Raise a defect. Operate a specifically delegated non-production gate. Security verifies that unapproved actions fail, including attempts to access production data or bypass a release approval. Record owner, reviewer, observed outcome, and expiry for each test.
Run an Environment-Recovery Drill
Precondition: a safe non-production environment with an approved exercise window and documented recovery plan.
Action: introduce a controlled environment issue. Have incoming QA identify the affected dependency, gather redacted evidence, invoke the correct permitted recovery or escalation, confirm service health, and rerun the smoke suite.
Expected: no unauthorized destructive action. Clear handoff to DevOps when administrative rights are retained internally. Traceable recovery evidence. A blocked or unsafe recovery attempt must create a transition defect, not a workaround using an outgoing vendor account.
Phase 4: Transfer Domain Knowledge Through Demonstration and Teach-Back
Build a Domain Knowledge Map
Prioritize critical user journeys, roles, business rules, state changes, integrations, boundary conditions, historical incidents, and known exceptions. Map each topic to an outgoing subject-matter expert, receiving engineer, client domain approver, and practical verification exercise. The list must reflect the product’s risks rather than training attendance alone.
Use Real Defects and Releases as Teaching Material
Review permission-cleared prior incidents, root-cause analysis, change risk, escaped-defect patterns, and deployment decisions. Ask the incoming team to explain why a bug mattered and which missing condition should become a regression case. Do not expose confidential client examples in a public article or unapproved third-party training environment.
Progress From Shadowing to Reverse Shadowing
Use four levels.
Outgoing team demonstrates.
Incoming team executes with guidance.
Incoming team leads while the current owner observes, which is reverse shadowing.
Incoming team performs independently with the old owner only on an agreed escalation channel.
Google’s operational-takeover guidance supports staged responsibility and temporary advisory cover, though the length of the period is engagement-specific.
Use Teach-Back as the Acceptance Mechanism
Precondition: the receiving tester has completed the authorized walkthrough.
Action: explain one high-risk workflow and its business rules. Select happy-path, negative, and boundary tests. Run a representative case. Identify a seeded defect. Describe the correct escalation and release-risk implication.
Pass: the domain owner accepts accuracy without substantial prompts. Evidence links to the demonstration and the recorded corrections. For critical functions, appoint an appropriately trained backup where team size and risk justify one. This is not a universal staffing quota.
Phase 5: Transfer Release Ownership One Gate at a Time
Inventory Every Quality and Deployment Gate
List smoke and regression checks, performance, security, and accessibility checks only where contracted, CI branch policies, artifact and environment checks, test evidence requirements, manual approvals, business exceptions, and emergency procedures. Map each gate to the administrator, execution owner, approver, and backup. Azure Pipelines, for example, allows approval and check policies to be set on protected resources by their administrators independently from pipeline YAML.
Define What a QA Release Recommendation Means
Require a report identifying build, environment, critical journeys, planned and executed tests, exclusions, blocked tests, unresolved severity and impact, automation health, evidence links, and residual risk. Define four possible recommendations: Ready, Ready with named risk acceptance, Not ready, or Unable to assess. Define no-go triggers before the rehearsal, for example a missing critical authorization test or an unapproved bypass. Never substitute a raw pass-rate percentage for these conditions.
Transfer Approver and Administrative Roles Deliberately
Maintain an approver register covering gate, administrative owner, approved approver and deputy, permissions, required evidence, escalation path, expiry, and break-glass procedure. Ask client-side release governance to verify the final go or no-go authority. Incoming QA may prepare the evidence and recommend readiness, but business risk acceptance stays with the designated client owner unless validly and explicitly delegated.
Rehearse Failure and Rollback Paths
Illustrative release exercise: a seeded blocking regression causes CI to fail. QA opens an evidence-linked defect. Engineering prepares a fix. QA retests affected areas. The release manager verifies no-go or recovery. A non-production rollback is rehearsed under the permitted change procedure. Repeat for an incomplete suite, unavailable integration, or rejected approval where those risks are material. Verify both prevention of an unsafe release and a clear recovery route.
Preserve Separation Between QA Readiness and Business Release Authority
Document three separate approvals.
QA acceptance of test evidence.
Technical approval to deploy.
Business acceptance of residual risk.
Some organizations combine roles under policy. The important control is that named authorized decision-makers agree and the audit trail shows the actual decision. Outsourcing testing is not, by itself, delegation of production authorization.
Phase 6: Cut Over Through Controlled Parallel Operation
Run a Representative Release With Both Teams Present
Agree the cutover owner, effective date and time zone, outgoing-team availability, release coverage, asset custody, open-ticket inventory, client-owned work queues, service continuity plan, and fallback decision authority. For first-time outsourcing, internal QA may supply the overlap. For vendor replacement, additionally verify the incumbent’s contractual exit assistance, transfer permissions, asset ownership, agreed overlap, data return or deletion, and ability to withdraw access without interrupting delivery.
Let the Incoming Team Lead the Next Release
During reverse shadowing, the receiving team plans and executes risk-based coverage, prepares data, diagnoses failures, writes defect evidence, maintains a test or CI configuration, reports release readiness, and joins the approval discussion. The outgoing team observes rather than quietly doing the hard steps. A single easy smoke cycle is inadequate for a system whose release-critical flows depend on multiple integrations, platforms, or recovery procedures. Select rehearsals proportionate to risk.
Record Interventions Required From the Outgoing Team
Use an intervention log: activity, missing knowledge or permission, who assisted, operational impact, corrective owner, retest, and closure evidence. Separate permissible subject-matter consultation from an undocumented critical dependency. Repeated interventions block cutover of the affected capability until the receiving team proves independence.
Repeat or Delay Cutover Where Unresolved Dependencies Remain
Use an explicit go or no-go meeting. If a mandatory gate fails near the contract change date, do not mark it passed. Keep the relevant responsibility with the authorized incumbent or internal owner under an agreed continuity arrangement, delay the affected cutover, obtain a documented service extension or internal fallback as needed, and escalate unresolved contractual or operational risks. Do not assume the outgoing vendor is obligated to provide unpaid support after its agreed end date. Assign incoming and outgoing owners to every open defect, incident, test asset, and scheduled CI job. Prevent tickets from falling between systems.
Move the Outgoing Team to Advisory-Only Support Before Removing Access
After an incoming-led cycle passes, switch the outgoing team to agreed advisory cover. Confirm client custody of code, work items, pipelines, evidence, and historic archives. Revoke former user, device, and group access on the approved date. Rotate shared tokens where required. Revalidate CI and release gates after revocation. Obtain documented data return or deletion evidence consistent with contracts and applicable law. Keep any legally required retention archive under approved access controls. Review all residual transition risks with the client owner before administrative closure.
Use Explicit Exit Criteria Before Declaring the Transition Complete
The incoming team’s capability should be accepted per workstream, not through a single ceremonial signoff. A readiness scorecard can use Pass, Fail, Blocked, Accepted exception, or Not applicable, but exceptions must identify business impact, mitigating action, expiry, and the authorized risk owner. No generic numeric readiness score should override a failed critical control.
S. No
Gate
Pass evidence
Evaluator and final approver
1
Asset custody and coverage
Reconciled register, critical journeys mapped, history archived
QA lead and client transition sponsor
2
Automation independence
Clean checkout, CI, diagnostic, and reviewed maintenance change
Automation SME and client QA lead
3
Data and access
Authorized role test, MFA, approved data use, evidence controls
Security and data owner, client sponsor
4
Environment operations
Safe recovery or escalation drill and retest
Platform owner and release lead
5
Domain competence
Accepted teach-back and seeded-defect triage
Product owner and QA lead
6
Release decision rights
Failed gate blocked. QA report and final client go or no-go recorded
Release manager and named business approver
7
Cutover and offboarding
Incoming-led cycle, fallback agreed, outgoing access revoked or dated
Transition sponsor and security owner
Store sign-offs and supporting links in the organization’s approved system of record. A reviewer signature without its underlying test evidence does not satisfy the gate.
QA Outsourcing Transition Checklist
Copy the rows below into a tracker. The accompanying editable workbook provides separate fields for owner, due date, required evidence, status, unresolved risk, approver, and sign-off date. Mark a checkbox only when the proof has been reviewed. A blank approver or missing evidence is not a completed item.
S. No
Transition task
Required evidence and reviewer
1
Governance and contractual boundaries confirmed
RACI, scope, IP and exit checks where applicable. Client sponsor
2
QA asset and risk inventory reconciled
Signed register and coverage map. QA lead
3
Manual suites and retained history accessible
Sample migration reconciliation. QA lead
4
Automation independently built, run, and amended
CI run, review request, and diagnosis. Automation lead
5
Test-data generation and cleanup verified
Authorized data drill and retention plan. Data owner
6
Access, MFA, least privilege, and expiry recorded
Approved role test and audit path. Security owner
7
Environment failure path rehearsed
Recovery or escalation evidence. Platform owner
8
Critical domain journeys passed teach-back
Exercise record. Product owner
9
Defect triage and evidence sharing verified
Reproduction and redacted report. Defect lead
10
QA readiness and client release authority rehearsed
Failed-gate rehearsal and decision record. Release manager
11
Incoming team led a risk-representative cycle
Intervention log and accepted report. Sponsor
12
Fallback, offboarding, and data disposition approved
Cutover decision, access plan, return or deletion evidence. Sponsor and security
Tracker statuses: Not started, In progress, Blocked, Pass, Fail, Accepted exception, Not applicable. Use Accepted exception only with a named risk owner, explanation, mitigation, expiry, and authorization. If a gate has a mandatory no-go rule, it cannot be waived by an unauthorized checklist editor.
Common Transition Failures and How to Diagnose Them
S. No
Symptom
Verification and corrective action
Release implication
1
Test count matches, but coverage drops
Rebuild risk-to-journey mapping. Reconcile shared steps and removed cases
Critical behavior may be untested
2
Automation only runs under an old vendor identity
Clean-room CI run. Replace runner and service-account dependencies
Loss of test capability after exit
3
Incoming team can execute but not triage
Seed a reproducible integration failure. Review domain and observability gaps
Longer diagnosis and weak risk reporting
4
Release approval has no clear owner
Trace gates and approvers. Rehearse a rejected deployment
Unauthorized or stalled deployment
5
Shared environment resets disrupt teams
Check operator permissions, change window, and rollback prerequisites
Environment and delivery disruption
6
Historical evidence disappears
Reconcile old runs and approved archive access
Audit and debugging blind spots
7
Defect attachments leak sensitive data
Inspect redaction, access controls, and retention. Remediate storage
Security and privacy incident risk
8
Contract ends before incoming independence
Invoke the pre-agreed internal or incumbent continuity path. Defer affected cutover
Loss of coverage at release time
Conclusion
A successful QA outsourcing transition leaves the next team capable of independently performing the agreed QA work and leaves the client in control of release decisions, sensitive information, and supplier exit. Begin with the ownership matrix, assign the checklist, and test the handover before authorizing cutover. For organizations evaluating an external testing relationship, Codoid describes its QA outsourcing services and its outsourced mobile testing scope and deliverables guide. The acceptance criteria should still be tailored to the product and contract rather than assumed from a standard package.
Need Help Planning Your QA Outsourcing Transition?
What should be included in a QA outsourcing handover?
Include the ownership matrix, active test assets and traceability, automation source and CI dependencies, test environments and accounts, data controls, product knowledge, defect and reporting processes, release gate permissions, acceptance evidence, fallback plan, and outgoing access or data disposition.
How do you know knowledge transfer is complete?
The receiving tester must teach back a critical workflow, select appropriate positive, negative, and boundary coverage, diagnose a seeded defect, and explain correct escalation without material undocumented help. Obtain domain-owner acceptance and retain the evidence.
Should the outgoing and incoming QA teams overlap?
Usually, some agreed overlap supports shadowing, reverse shadowing, rehearsal, and continuity. Its duration should follow product risk and demonstrated independence, not an assumed universal number of weeks. Vendor replacement also requires a contractually feasible exit plan.
Who should own automated test code after outsourcing?
Define code rights, repository custody, maintenance responsibility, dependencies, CI runners, licenses, and portability in the agreement and operational register. The receiving team should be able to modify and run the agreed assets using approved accounts.
Should a QA outsourcing provider own release sign-off?
Not by default. A QA partner may recommend readiness and operate explicitly delegated checks, but the client's named authorized person makes the final production go or no-go and accepts business risk unless formal governance delegates otherwise.
How should test environments and credentials be transferred?
Transfer environment knowledge, not passwords. Provision approved roles and service identities with MFA, least privilege, logging, expiry, and revocation. Validate them through task-based tests. Use synthetic or authorized minimized data and protected evidence storage.
What should happen to old vendor access after cutover?
Confirm replacement identities and ownership first. Then revoke outgoing accounts and device access, rotate shared secrets where required, verify pipelines still run, and document data return or deletion plus any approved retention exceptions.
How do you transition QA without pausing releases?
Transfer capabilities in risk order, maintain an agreed coverage owner during overlap, rehearse an incoming-led release and failed gate, and cut over only when each mandatory gate is accepted. If a gate fails, invoke the pre-authorized continuity arrangement instead of silently accepting the gap.
Flutter automation testing has become increasingly important as Flutter continues to establish itself as a powerful framework for building cross-platform mobile and web applications. Introduced by Google in May 2017, Flutter is still relatively young compared to other frameworks. However, despite its short history, it has gained rapid adoption due to its ability to deliver high-quality applications efficiently from a single codebase. Flutter allows developers to write code once and deploy it across Android, iOS, and Web platforms, significantly reducing development time and simplifying long-term maintenance. To ensure the stability and reliability of these cross-platform apps, automation testing plays a crucial role. Flutter provides built-in support for automated testing through a robust framework that includes unit, widget, and integration tests, allowing teams to verify app behavior consistently across platforms. Tools like flutter_test and integration with drivers enable comprehensive test coverage, helping catch regressions early and maintain high quality throughout the development lifecycle. In addition to productivity benefits, Flutter applications offer excellent performance because they are compiled directly into native machine code. Unlike many hybrid frameworks, Flutter does not rely on a JavaScript bridge, which helps avoid performance bottlenecks and delivers smooth user experiences.
As Flutter applications grow in complexity, ensuring consistent quality becomes more challenging. Real users interact with complete workflows such as logging in, registering, checking out, and managing profiles, not with isolated widgets or functions. This makes end-to-end automation testing a critical requirement. Flutter automation testing enables teams to validate real user journeys, detect regressions early, and maintain quality while still moving fast.
In this first article of the series, we focus on understanding the need for automated testing, the available automation tools, and how to implement Flutter integration test automation effectively using Flutter’s official testing framework.
Why Automated Testing Is Essential for Flutter Applications
In the modern business environment, product quality directly impacts success and growth. Users expect stable, fast, and bug-free applications, and they are far less tolerant of defects than ever before. At the same time, organizations are under constant pressure to release new features and updates quickly to stay competitive.
As Flutter apps evolve, they often include:
Multiple screens and navigation paths
Backend API integrations
State management layers
Platform-independent business logic
Manually testing every feature and regression scenario becomes increasingly difficult as the app grows.
Challenges with manual testing:
Repetitive and time-consuming regression cycles
High risk of human error
Slower release timelines
Difficulty testing across multiple platforms consistently
How Flutter automation testing helps:
Validates user journeys automatically before release
Ensures new features don’t break existing functionality
Supports faster and safer CI/CD deployments
Reduces long-term testing cost
By automating end-to-end workflows, teams can maintain high quality without slowing down development velocity.
Understanding End-to-End Testing in Flutter Automation Testing
End-to-end (E2E) testing focuses on validating how different components of the application work together as a complete system. Unlike unit or widget tests, E2E tests simulate real user behavior in production-like environments.
Flutter integration testing validates:
Complete user workflows
UI interactions such as taps, scrolling, and text input
Navigation between screens
Interaction between UI, state, and backend services
Overall app stability across platforms
Examples of critical user flows:
User login and logout
Forgot password and password reset
New user registration
Checkout, payment, and order confirmation
Profile update and settings management
Failures in these flows can directly affect user trust, revenue, and brand credibility.
Flutter Testing Types: A QA-Centric View
Flutter supports multiple layers of testing. From a QA perspective, it’s important to understand the role each layer plays.
S. No
Test Type
Focus Area
Primary Owner
1
Unit Test
Business logic, models
Developers
2
Widget Test
Individual UI components
Developers + QA
3
Integration Test
End-to-end workflows
QA Engineers
Among these, integration tests provide the highest confidence because they closely mirror real user interactions.
Flutter Integration Testing Framework Overview
Flutter provides an official integration testing framework designed specifically for Flutter applications. This framework is part of the Flutter SDK and is actively maintained by the Flutter team.
This flexibility allows teams to reuse the same automation suite across platforms.
Logging and Failure Analysis
Logging plays a critical role in automation success.
Why logging matters:
Faster root cause analysis
Easier CI debugging
Better visibility for stakeholders
Typical execution flow:
LoginPage.login()
BasePage.enterText()
BasePage.tap()
Well-structured logs make test execution transparent and actionable.
Business Benefits of Flutter Automation Testing
Flutter automation testing delivers measurable business value.
Key benefits:
Reduced manual regression effort
Improved release reliability
Faster feedback cycles
Increased confidence in deployments
S. No
Area
Benefit
1
Quality
Fewer production defects
2
Speed
Faster releases
3
Cost
Lower testing overhead
4
Scalability
Enterprise-ready automation
Conclusion
Flutter automation testing, when implemented using Flutter’s official integration testing framework, provides high confidence in application quality and release stability. By following a structured project design, applying clean locator strategies, and adopting QA-focused best practices, teams can build robust, scalable, and maintainable automation suites.
For QA engineers, mastering Flutter automation testing:
Reduces manual testing effort
Improves automation reliability
Strengthens testing expertise
Enables enterprise-grade quality assurance
Investing in Flutter automation testing early ensures long-term success as applications scale and evolve.
Frequently Asked Questions
What is Flutter automation testing?
Flutter automation testing is the process of validating Flutter apps using automated tests to ensure end-to-end user flows work correctly.
Why is integration testing important in Flutter automation testing?
Integration testing verifies real user journeys by testing how UI, logic, and backend services work together in production-like conditions.
Which testing framework is best for Flutter automation testing?
Flutter’s official integration testing framework is the best choice as it is stable, supported by Flutter, and CI/CD friendly.
What is the biggest cause of flaky Flutter automation tests?
Unstable locator strategies and improper handling of asynchronous behavior are the most common reasons for flaky tests
Is Flutter automation testing suitable for enterprise applications?
Yes, when built with clean architecture, Page Object Model, and stable keys, it scales well for enterprise-grade applications.
ExtentReport has been a well-liked tool for creating regular email reports for years. Reporting is very important in test automation. It helps teams check results, spot problems, and make better choices. However, with advancements in automation testing happening at a rapid pace, old reporting tools are having trouble meeting the new needs for real-time updates, active dashboards, and better analysis. This is where ChainTest Report helps. Made for today’s test automation needs, ChainTest goes past regular reports. It offers real-time data, interactive dashboards, and better teamwork for testing groups. As automation moves to quicker integration and delivery, having a strong and flexible reporting tool is more important than ever.
This blog looks at how ChainTest changes test reporting. It explains why it is a great choice for teams that want to keep up in the fast-evolving world of automation testing.
Key Highlights
Say goodbye to ExtentReport and welcome ChainTest for better Selenium reporting.
Access real-time analytics and track historical data for smart insights.
Enjoy easy connection with popular test frameworks like JUnit, TestNG, and Cucumber. PyTest support is coming soon.
Make reporting easier with simple setup, Docker support, and a friendly interface.
Get ahead in automation testing with thorough, attractive, and informative reports.
Key Features of ChainTest
Real-Time Analytics: Teams can view their test runs as they happen, helping them quickly find and fix issues. Watching updates on test progress, like failures and successes, provides helpful insights.
Historical Data Storage: ChainTest saves past test runs, helping teams analyze trends and code changes to improve their strategies.
Simple Setup: Using Docker makes the setup process fast and hassle-free, so teams can focus on writing and executing tests instead of fixing dependencies.
Understanding the Basics of ChainTest and Selenium Integration
ChainTest and Selenium are great partners. They help you improve the quality of your testing work. ChainTest adds smart insights to Selenium. It records key details of your test runs and presents them clearly.
With ChainTest, you can make great reports for your Selenium tests. These reports show everything about your tests. They include helpful charts, logs, and screenshots. ChainTest also makes it easy to share your results with both technical and non-technical people.
Transitioning from ExtentReport to ChainTest is a major improvement for your Selenium reporting. ExtentReport was a solid beginning, but ChainTest goes beyond that. It offers better insights and a smoother experience for users.
Do you remember having problems with static test results and historical data? ChainTest fixes these issues. It provides dynamic, attractive reports and tracks your historical data effectively. ChainTest helps you explore your Selenium test results. You can discover hidden patterns and make smart decisions to enhance your testing.
ChainTest offers more. It provides real-time analytics. You can watch your tests as they happen. You don’t need to wait until test runs are over to get information. With ChainTest, you stay updated all the time. This allows you to find and fix issues faster. As a result, you enjoy quicker releases and a better product.
Setting Up Your Environment for ChainTest Reports
Are you ready to make your Selenium reporting better with ChainTest? The good news is that it’s simple to get started. ChainTest fits nicely with your existing Selenium test suites. It won’t change your workflow too much.
Setting it up is easy. You just need to install the right tools and set up Selenium to work with ChainTest. The process is simple, even if you are new to advanced reporting tools. Let’s improve your testing toolkit with ChainTest and find new ways to get helpful information.
Installing Necessary Dependencies
Before we begin creating great ChainTest reports, we need to prepare our environment.. Here is a step-by-step guide to help you.
First, choose a ChainTest repository that fits your testing framework. ChainTest works well with well-known frameworks like JUnit, TestNG, and Cucumber. Picking the right repository makes sure it works well with your current test setup.
Next, add the ChainTest dependency to your project easily. This helps your testing framework work better with the ChainTest server. It also makes it easy to create useful reports.
Finally, choose how you want to deploy the ChainTest server. A Docker image is a simple and fast option. It provides a pre-set environment, so you can get started quickly.
Step 1: Setting Up ChainTest in Selenium Project
First, you need to add ChainTest to your Selenium project. If you are using Maven, put this dependency in your pom.xml:
Generate Reports in Multiple Formats – Export as HTML, PDF, JSON, or XML.
Enable Email Notifications – Send reports automatically to stakeholders.
Integrate with CI/CD Pipelines – Share results via Jenkins, GitHub Actions, Azure DevOps, etc.
6. Customizing ChainTest Properties
Modify haintest.properties file to set default configurations:
chaintest.project.name=MyTestProject
chaintest.generator.chainlp.enabled=true
chaintest.generator.chainlp.class-name=com.aventstack.chaintest.generator.ChainLPGenerator
chaintest.generator.chainlp.host.url=http://localhost/
chaintest.report.format=HTML, PDF
chaintest.screenshot.storage=AWS_S3
Here’s an example setup that shows how different test frameworks work together. It also allows you to adjust the way the dashboard looks.
Configuration Key
Description
chaintest.project.name
Specifies the project name, enabling you to organize and filter reports effectively
chaintest.generator.chainlp
Dictates the module responsible for generating reports in various formats, such as HTML or PDF
Understanding Chain LP Generator in Chain Test Report
What is Chain LP?
Chain LP Generator is a report generator in Chain Test Report that enables real-time test reporting while maintaining a historical record of test executions.
How Does Chain LP Work?
ChainLP is a Spring Boot-based server with a front-end packaged as a Docker image. To generate Chain Test Reports using the Chain LP Generator, the Chain LP server must be running.
After configuring Chain LP, we can proceed to execute test cases. The results will be automatically stored and displayed in the Chain Test Report.
Viewing Test Results in Chain LP
To view test execution reports, open the URL defined in chaintest.generator.chainlp.host.url in a web browser.
Attaching Screenshots to Chain LP Reports on Failure
To attach screenshots of test failures in Chain LP Reports, use a cloud storage solution such as:
Azure Blob Storage
AWS S3 Bucket
Conclusion
In conclusion, learning ChainTest for Selenium is a great way to boost your test automation skills. It offers many benefits over ExtentReport. By using its main features, you can make your testing faster and smoother. Linking ChainTest with Selenium allows you to create detailed and helpful test reports.
To set up your environment for ChainTest reports, just install the necessary tools and configure Selenium easily. Use this powerful tool to improve your testing quality and obtain clear reports with no hassle.
For more help with ChainTest and Selenium, take a look at our FAQ section or reach out to our experts for personal support.
Frequently Asked Questions
How Does ChainTest Improve Selenium Test Reports?
ChainTest improves how Selenium test reports are made by adding real-time analytics. You get quick insights right away. It stores historical data which helps in looking at trends. It also makes detailed reports for better clarity. With these features, teams can enhance their automation work and boost software quality.
Can ChainTest Be Integrated With Existing Selenium Projects?
ChainTest works great with all types of Selenium projects. It has a flexible design that works well with popular testing tools, including Java Spring Boot. Setting it up is simple. This makes it a good choice to enhance the reporting features of your existing Selenium tests.
What Are the Key Benefits of Using ChainTest for Selenium Reporting?
ChainTest is a better option than ExtentReport for reporting in Selenium. It offers several advantages. Users can see real-time analytics and appealing dashboards. They can also check historical data. ChainTest helps users grasp their test results more clearly. It simplifies communication and allows them to make data-driven decisions. This can lead to ongoing improvement in their work. In summary, it boosts the success of their test automation efforts.
Is There a Learning Curve to Master ChainTest with Selenium?
ChainTest is easy to use. It has a friendly design and offers a lot of helpful information. It works well with common testing tools, making it simple to learn. Testers familiar with automation and Java can quickly grasp how it functions. They can start enjoying better reporting in no time
Test automation plays an important role in software development and quality assurance today, especially in the realm of software testing. This includes regression testing. However, if not managed properly, automated test suites can sometimes cost more than their benefits. To reduce test automation maintenance costs and improve maintenance efforts, it’s essential to follow best practices in the testing process and test design. A good approach to coding and fixing software defects during the development process can help lower maintenance work. This approach can also enhance the test plan and make changes easier when needed. By acting early, teams can keep their test automation with a good test automation tool efficient and useful over time.
This article gives helpful tips to lower maintenance costs in Automation Testing Service. It has stories to explain each tip clearly, along with practical advice that you can easily use.
Understanding Test Automation Maintenance Costs
Before we discuss strategies, we need to understand what influences maintenance costs in test automation. Here are some common factors:
Fragile Tests: These tests often fail due to small UI changes or unstable environments.
Over-Automation: This happens when we automate tasks that are not necessary, making things more complex without a good return.
Poor Test Design: This is about tests that are hard to reuse or change, causing the same tests to be repeated several times.
Flaky Tests: These tests sometimes pass and sometimes fail due to outside factors like timing issues or inconsistent dependencies.
Misaligned Tools: This is when we use tools or frameworks that do not fit well with our technology setup.
Addressing these problems requires good planning, using technical best practices, and creating a teamwork-focused culture.
1. Build a Strong Foundation with Effective Test Design
A good test design is key for a strong Automation Framework. Poorly designed tests can break easily. They may be hard to repeat and take a long time to fix. To keep maintenance costs down, teams should focus on:
Risk-Based Testing
Focus your automation efforts on high-risk areas that really matter for the application’s success.
For low-risk features or ones that are rarely used, manual testing might be enough.
Test Pyramid Principle
Adopt a layered testing strategy:
Unit Tests: These tests focus on individual pieces of the code. They are fast, reliable, and easy to manage.
Integration Tests: These tests check if services or modules communicate properly.
UI/E2E Tests: These tests focus on key workflows, often called “happy paths.” They help lower the chance of having weak UI actions.
Balanced Coverage
You do not have to automate everything.
Focus on the most important tasks and times that are hard to manage.
Add negative tests to ensure that the tests work well.
This keeps the test suite simple and focused.
2. Write Clean and Maintainable Test Code
Test automation code needs to follow good practices, just like regular production code. If test scripts are poorly written, it can create more work when updates are required.
Layered Architecture
Organize automation code into simple layers, like.
Page Objects keep the details of UI elements hidden.
Helper Methods let us reuse functions easily.
Data Management Layers take care of managing test data.
DRY Principle (Don’t Repeat Yourself)
Place actions that repeat into methods or base classes you can use again.
This helps reduce repetition.
It also simplifies making new tests.
For instance, if multiple tests need a login feature, put it in a shared utility.
This lets you avoid writing the login function in every script.
Use Patterns like POM or Screenplay
Page Object Model (POM) divides user interface (UI) elements into different classes. This helps keep the test logic apart from the UI locators.
Screenplay Pattern views user actions as tasks. This provides a clearer picture of each step in a test.
Readable Code
Clear naming rules and good test scripts help team members quickly understand and update tests. This makes it easier for them to manage the tests and lowers costs.
3. Optimize Locators and Application Design
Fragile locators can cause test failures.
A strong plan for locators and good teamwork with developers can reduce the need for maintenance a lot.
Stable Locators
Use tags like data-test-id or aria-label as good selectors.
Avoid weak locators, such as long XPath expressions. They usually break with small UI changes.
Test-Friendly Application Design
Work with developers to build applications that are easy to test.
Adding stable IDs or test hooks during development can make automation better.
This practice makes it less likely to fail.
Minimize UI Dependence
Try to test functions using APIs or service layers when you can.
This practice reduces the chances of issues with the UI.
It also allows you to get faster feedback.
4. Integrate Automation into CI/CD Pipelines
Continuous integration and deployment, known as CI/CD, are essential for keeping automated test groups running smoothly, preventing downtime. A good integration process decreases the need for human work. It also ensures that feedback arrives quickly.
Regular Test Execution
Automate test runs in CI pipelines to find problems early.
Running tests often helps catch failures before they turn into bigger issues.
Parallel Execution
Running tests at the same time makes the tests finish faster.
This way, you get feedback quicker.
It is really useful for large test suites.
Smart Test Selection
Use tools for test impact analysis.
These tools can identify and run only the tests that recent code changes affect.
This practice helps to avoid running all tests.
It saves time and resources.
5. Invest in Robust Reporting and Monitoring
Clear and helpful reports are very important. They help us find and solve problems quickly. If we don’t have the right information, it can take a lot of time and money to understand why tests do not pass.
Detailed Reports
Look for tools that provide full failure reports.
Ensure they have all important details.
Screenshots of tests that failed.
Logs that show stack traces for fixing problems.
Old data to track trends.
Monitor Flaky Tests
Track and find flaky tests.
This helps keep trust in your automation suite strong.
Fixing these issues fast will save money on maintenance in the long run.
Test automation is not a one-time task. It requires constant investment. This supports its ability to adjust to changes in the application and the needs of the business.
Regular Refactoring
Schedule regular reviews to check for and remove outdated or unnecessary tests.
Refresh weak scripts to match current standards.
Stay Aligned with Development Changes
Work closely with development teams.
Keep an eye out for upcoming changes.
Modify test scripts as needed.
Encourage Shared Ownership
Put test automation engineers in development teams. This helps everyone share the job of test maintenance.
Working together lowers the barriers between teams. It also makes things more efficient.
7. Choose the Right Tools and Technologies
Choosing the right tools is key to keeping costs down in test automation maintenance. The best tools make development, execution, and reporting simpler.
Tool Compatibility
Pick tools that fit your team’s technology.
This will help cut down problems when linking systems.
It will also save time needed to learn how to use them.
Mature Frameworks
Pick popular tools such as Selenium, Playwright, or Appium.
These tools have a lot of guides and support.
Many people use them.
You can find lively groups around these tools.
They receive regular updates.
This keeps them from becoming old and unused.
Cloud and Containerized Environments
Using cloud-based or container environments makes it easier to keep things consistent during test runs. This helps to lessen issues that can occur due to different settings.
Conclusion
Minimizing the costs of keeping test automation solutions up and running needs a full approach. This means careful planning, technical skills, and good teamwork.
A strong test automation strategy helps with web application testing. Good test design, code that is easy to maintain, and stable locators paired with AI testing tools ensure we cover all tests and achieve comprehensive test coverage while evaluating ROI effectively. This cuts down on issues and complexity. It also helps teams deliver new features that enhance user experience (UX).
When adding automation to CI/CD pipelines for web applications, it is crucial to think about the right factors. Paying attention to unstable tests and choosing the right automation tools can make everything more efficient.
A good test automation suite can save you time and money. It helps build trust in how the software is delivered. This practice enhances overall QA methods. Regular maintenance is an important long-term investment. It helps keep new features stable in the app. When done correctly, test automation is a vital tool. It allows for faster release cycles and higher quality software. This gives teams extra time to innovate, especially when they look at test results.
In our connected world, APIs are important for many applications. They allow simple websites and complex systems to work well. To make sure our applications are strong and reliable, we need to test these APIs properly, including services like OpenCage. This ensures they function correctly. This is where Bruno comes in! Whether you want to test a simple REST API or a complex geocoding API for happy geocoding, Bruno has the tools you need. It even has a directory for managing your API needs, along with a Bruno tutorial to guide you step-by-step in setting up and executing tests. This makes Bruno an accessible, powerful solution for ensuring your APIs are always reliable and effective.
Key Highlights of this Bruno Tutorial Study
Bruno is a strong tool for API testing. It makes designing, fixing, and handling API requests easier.
This open-source tool has a simple interface. It helps both new and experienced testers to get started quickly.
With Bruno, you can write test scripts using JavaScript. You can also use environment variables to handle different testing cases well.
The tool helps you move from other tools like Postman and Insomnia easily. This makes it simple for current users to switch.
Bruno also makes API testing easy within CI/CD pipelines. You can connect it with platforms like GitHub Actions for automatic testing jobs.
Git-based API collection management
Local-first API testing workflow
Better security with local storage
Easy integration with development workflows
Understanding the Basics of API Testing with Bruno
Before we talk about how to use Bruno, let’s go over the basics of API testing. API testing helps us see how an API functions and how secure it is. We do this by examining its endpoints and looking at the responses.
Bruno makes things simple. It is a full platform that lets you create, send, and check API requests easily. This helps you test different parts of your API without any trouble. It is a handy tool for developers and quality assurance workers. For those getting started, a Bruno tutorial can guide you through the features and functionalities, helping you make the most of the platform.
What is API Testing and Its Importance?
API testing is when we send requests to an API endpoint and check the answers we get back. This shows us if it functions as it should. This type of testing is different from UI testing, which looks at the user interface. API testing focuses on the main logic and how data flows in the application.
API testing is important in software development. It helps find bugs early. This builds trust in the data shared between systems. It also speeds up the development process. A strong set of API tests keeps your application reliable. This way, users have a better experience.
API testing is very important in today’s methods, like microservices. In this way of working, applications rely on several connected services. These services communicate with each other through APIs. It is vital to test these connections to ensure the system works well and stays stable.
Overview of Bruno for API Testing
Bruno is a free and open-source tool for API testing. It works well, especially when you compare it to well-known tools like Postman. You can use it on your desktop if you are using Windows, macOS, or Linux. The interface is simple to use, making it easy for anyone to handle complex API testing tasks.
With Bruno, you can create and organize API requests into groups. This helps you see your tests clearly. You can use different methods to make requests, like GET, POST, PUT, and DELETE. Each request allows you to control its headers and parameters. You can also change the request body for better testing.
Bruno is special because it focuses on making API testing easy on Mac. You can do more than just send requests. You can also check the response body, status codes, and headers of the API client. Bruno even has a save button for requests and collections. With this feature, you won’t lose your work. You can focus on building and adjusting your test suites without any hassle.
Reduce sync issues commonly seen in cloud-based tools
Keep API tests aligned with development workflows
Getting Started with Bruno Tutorial: A Beginner’s Guide
Starting your API testing journey with Bruno is easy. This guide is great for beginners. It will help you install Bruno and set up your first API test. You will also learn the basics of testing in a professional way.
When you follow these simple steps, you can use Bruno’s power. You can improve your development work by adding good API testing. This will help make sure your applications are high quality and reliable.
Prerequisites for Using Bruno in API Testing: In This Bruno Tutorial
Before you use Bruno, make sure you have a few things prepared. This will help ensure your testing process runs smoothly and efficiently. In this Bruno tutorial, we’ll guide you through the setup and essential steps to get started with the platform.
Project Folder: It is smart to make a project folder just for your API testing. This keeps your tests tidy and makes it easier to work with others if you are in a team. So, make a new folder on your computer to keep your Bruno tests.
Node.js and npm: Bruno needs Node.js and npm (Node Package Manager) to work. Check that these are installed on your computer. You can download the latest versions from the official Node.js website.
Bruno CLI (Command Line Interface): Bruno has a friendly interface, but knowing the Bruno CLI can help you automate your tests. This is useful if you want to connect it to CI/CD pipelines. To install the Bruno CLI, type this npm command: npm install @usebruno/cli –save-dev.
Step 1: Install Bruno
Download Bruno from its official site (bruno.io) or GitHub repository, depending on your OS.
Follow the installation prompts to set up the tool on your computer.
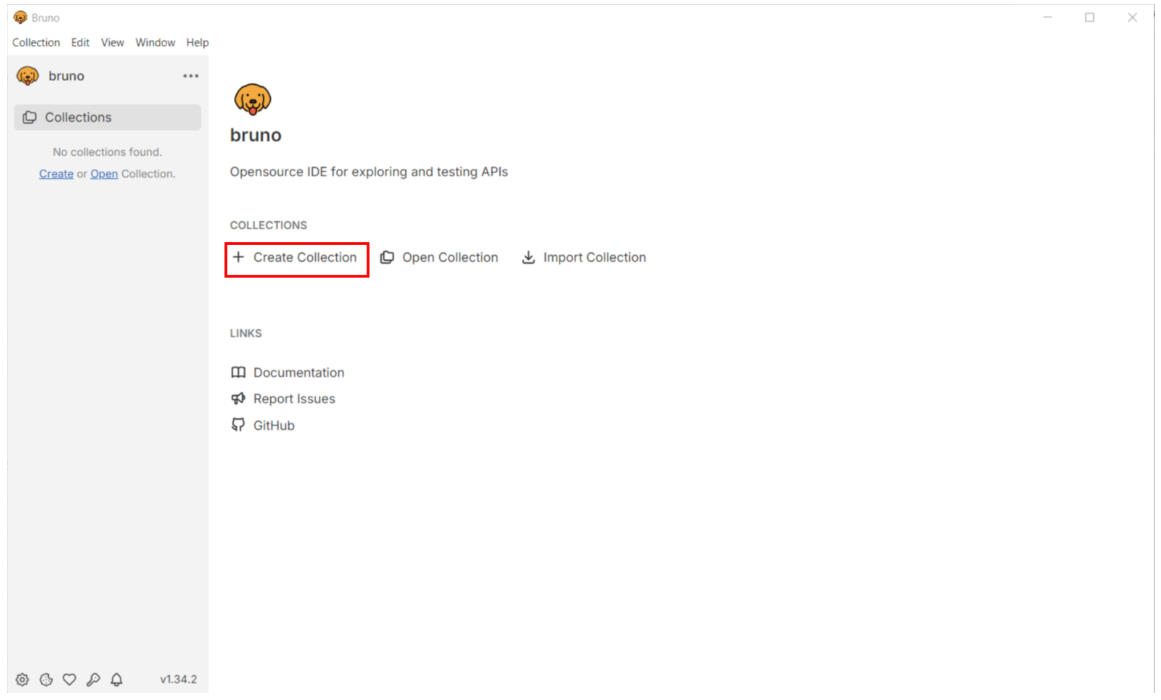
Step 2: Set Up an API Collection
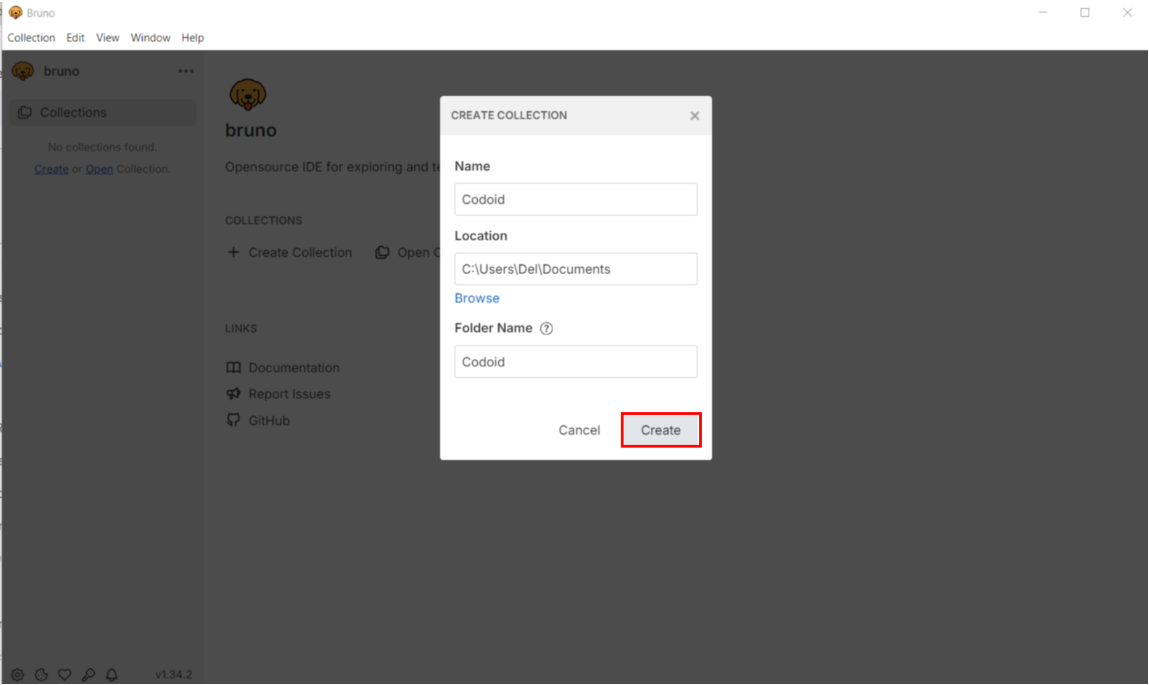
In your collection, create an API collection. Collections are groupings of related API requests.
Name your collection based on the API endpoints or service (e.g., “User Authentication API”).
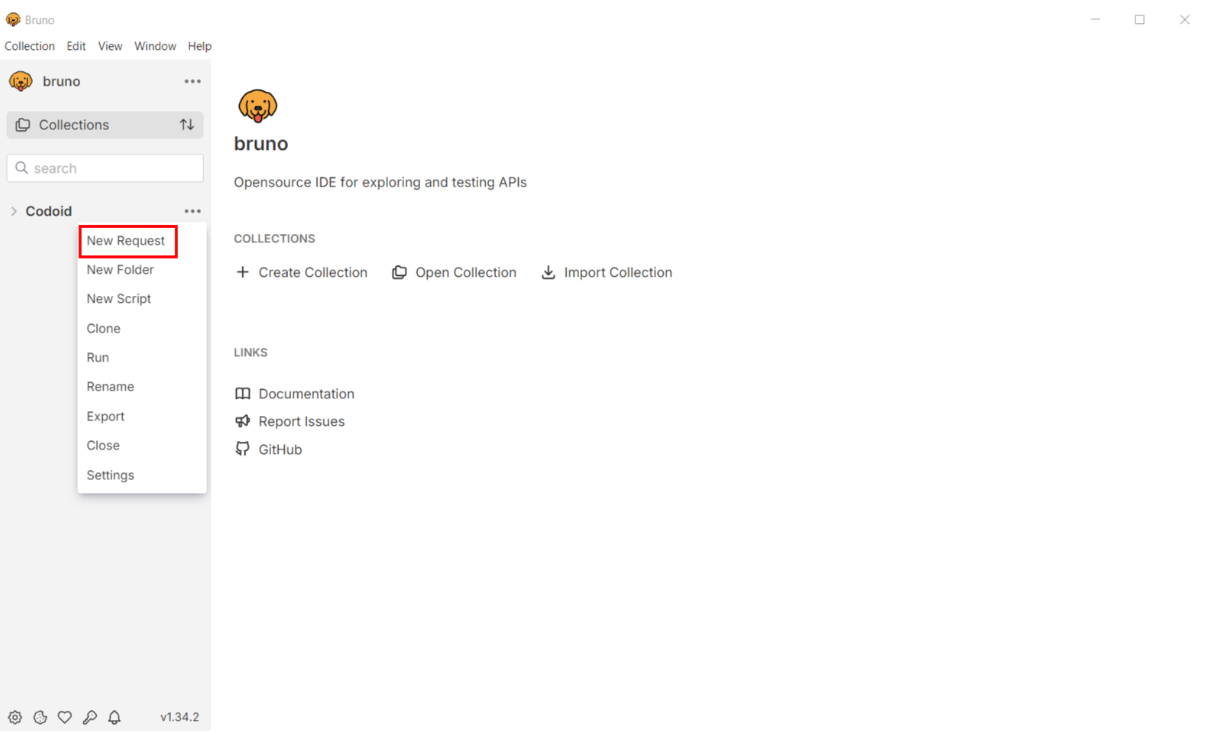
Step 3: Add an API Request
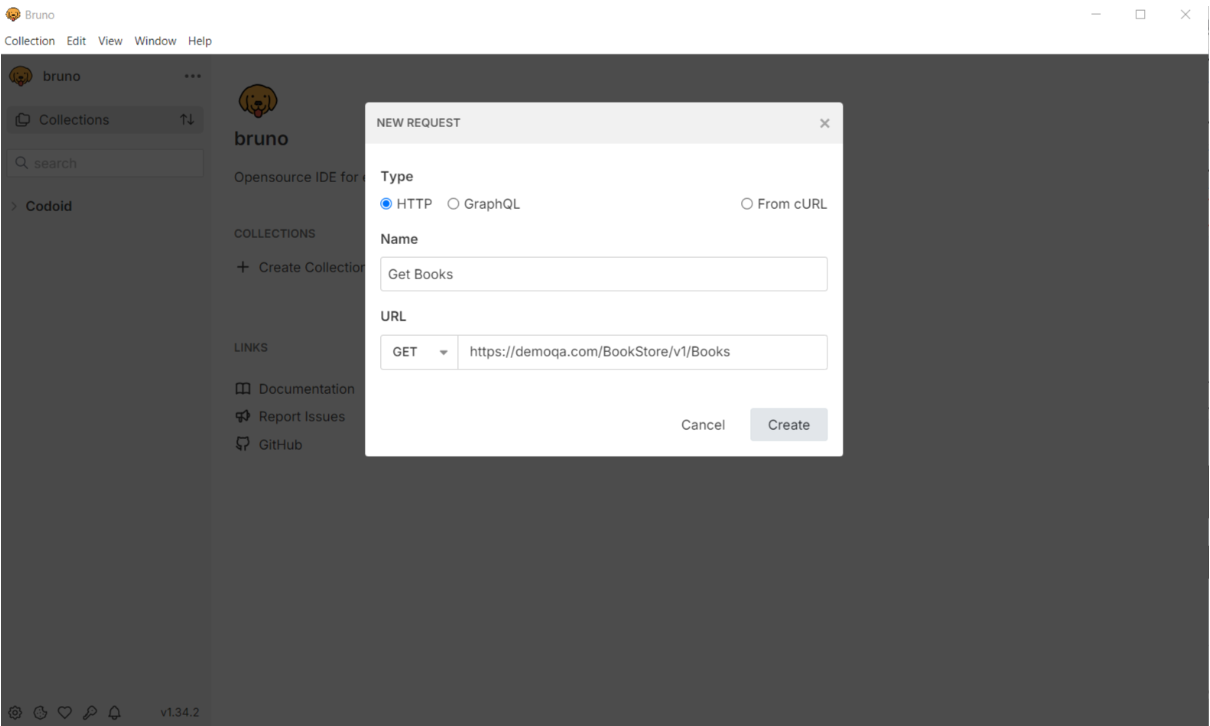
Inside the collection, click to add a new request.
Choose the HTTP method (e.g., GET, POST, PUT, DELETE) based on the API endpoint you’re working with.
Enter the API endpoint URL. If your API requires parameters or query strings, you can add them here.
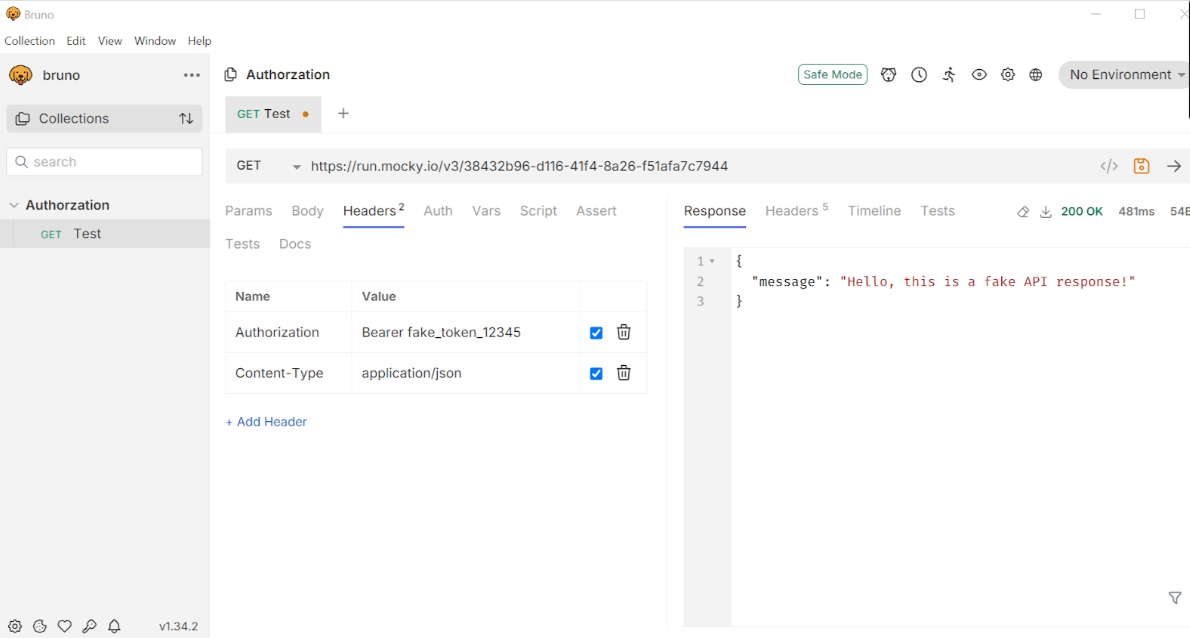
Step 4: Configure Request Headers
In the request section, configure any necessary headers (e.g., Content-Type, Authorization, etc.).
Bruno allows you to enter headers in YAML, so you can structure it like:
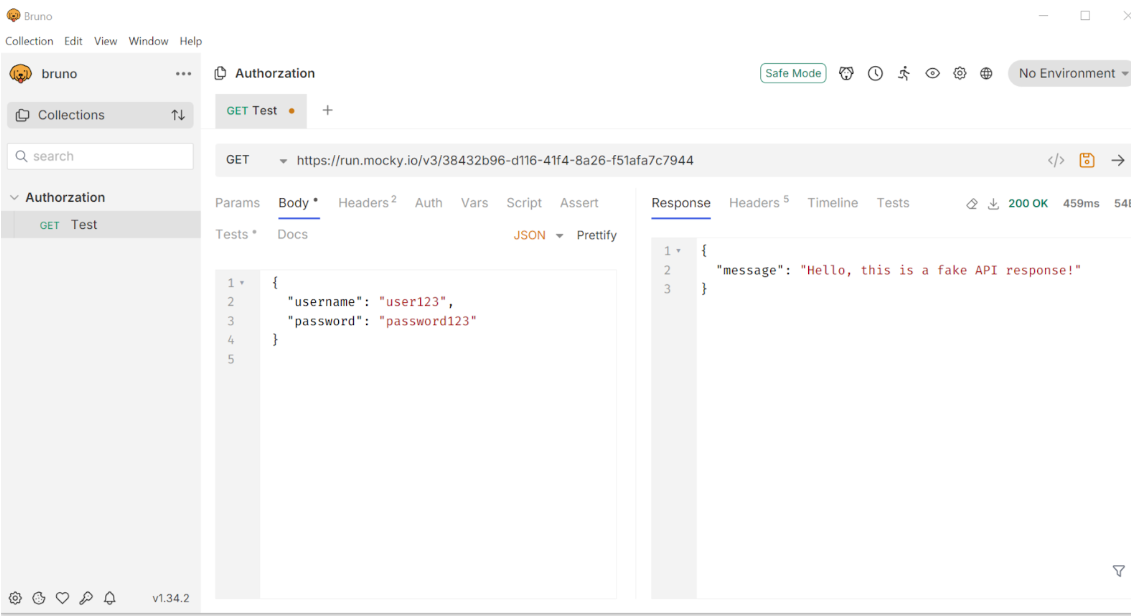
If you’re making a request that requires a body (such as POST), enter it in JSON or YAML format.
Example JSON body:
{
“username”: “user123”,
“password”: “password123”
}
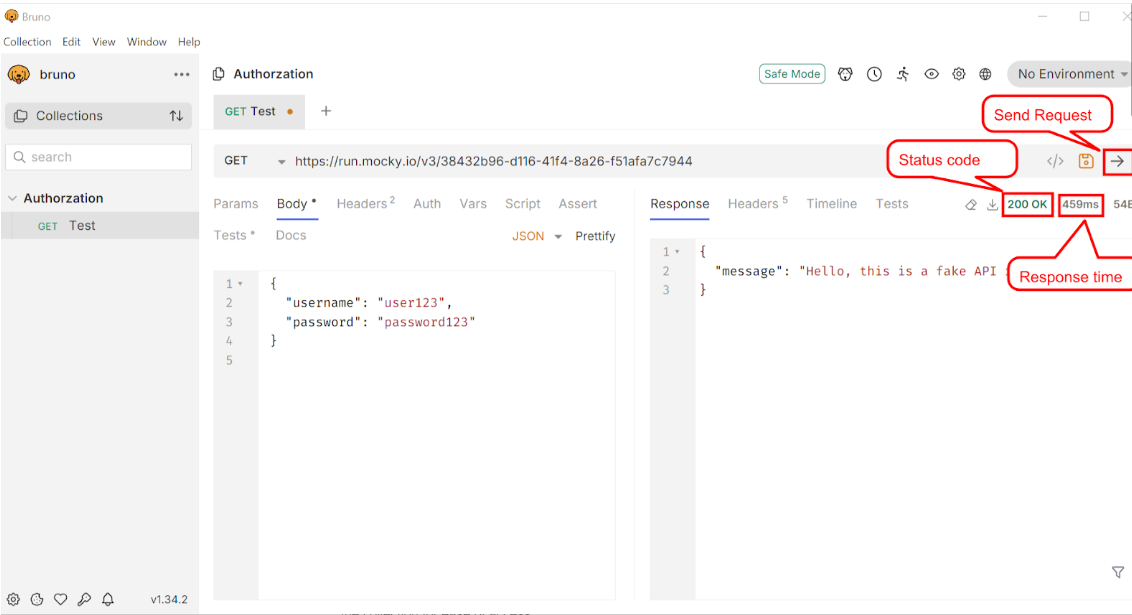
Step 6: Run the Request
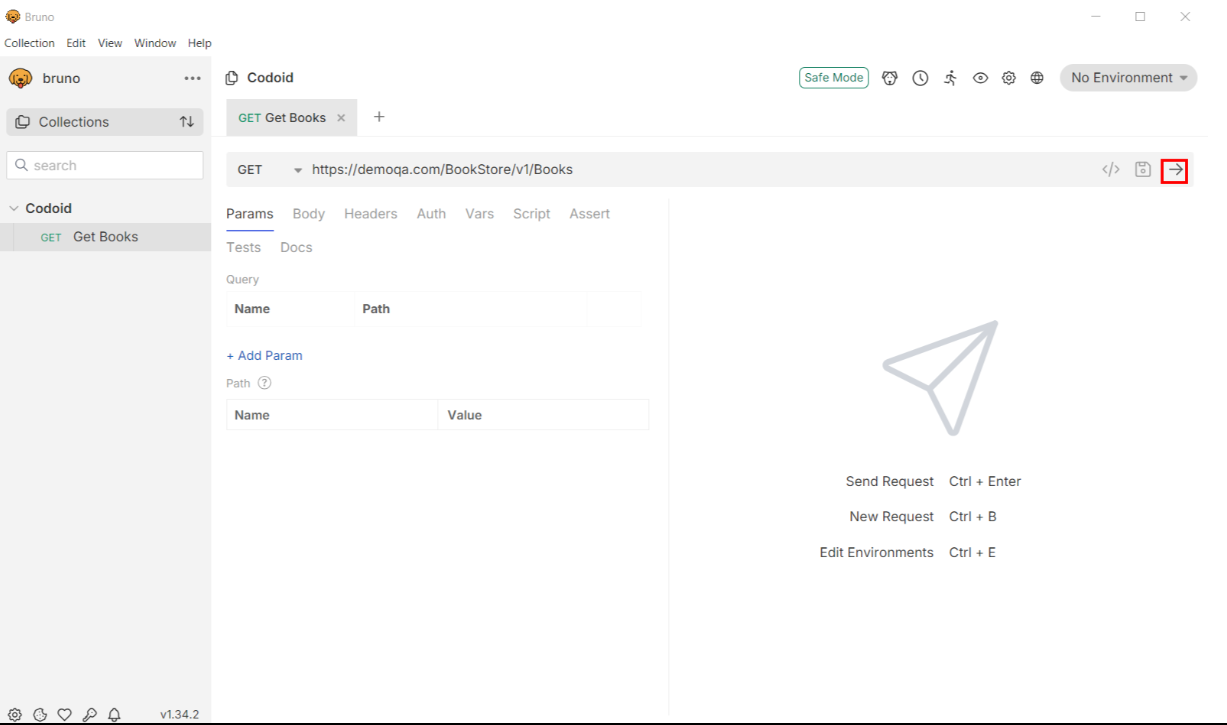
Once everything is set up, click Send to execute the request.
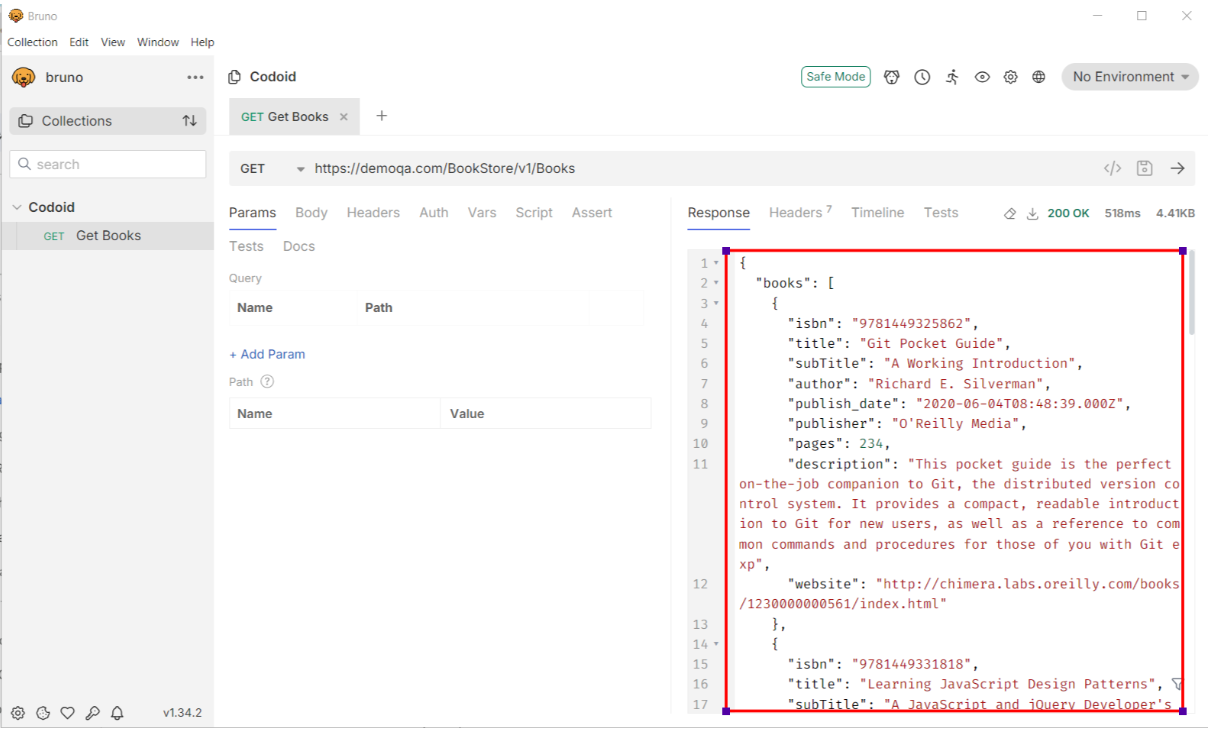
Bruno will show the response from the server, including status codes, headers, and the response body.
Step 7: View and Analyze the Response
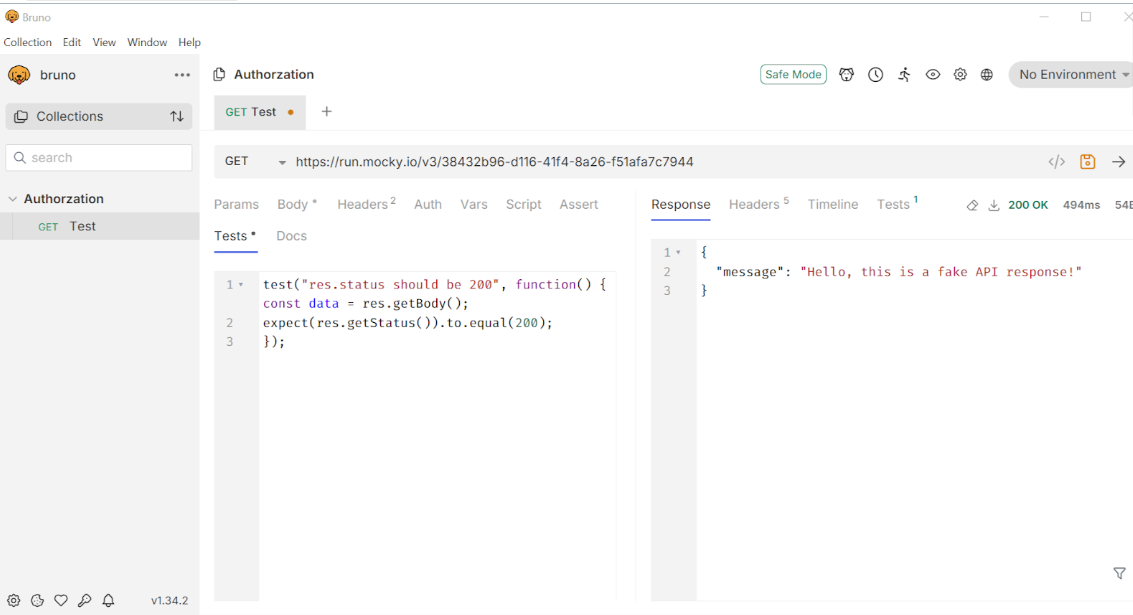
Review the server’s response to ensure it matches your expectations (e.g., status code 200 OK for a successful GET request).
Check response times, headers, and body to verify the API’s behavior.
Step 8: Save and Organize Requests
Save requests in the collection for reuse. Organize requests by grouping them logically within the collection for ease of access.
Step 9: Add Tests (Optional)
Bruno allows you to write test scripts to validate responses automatically.
Add assertions to ensure responses meet certain criteria (e.g., status code is 200, response contains a specific field).
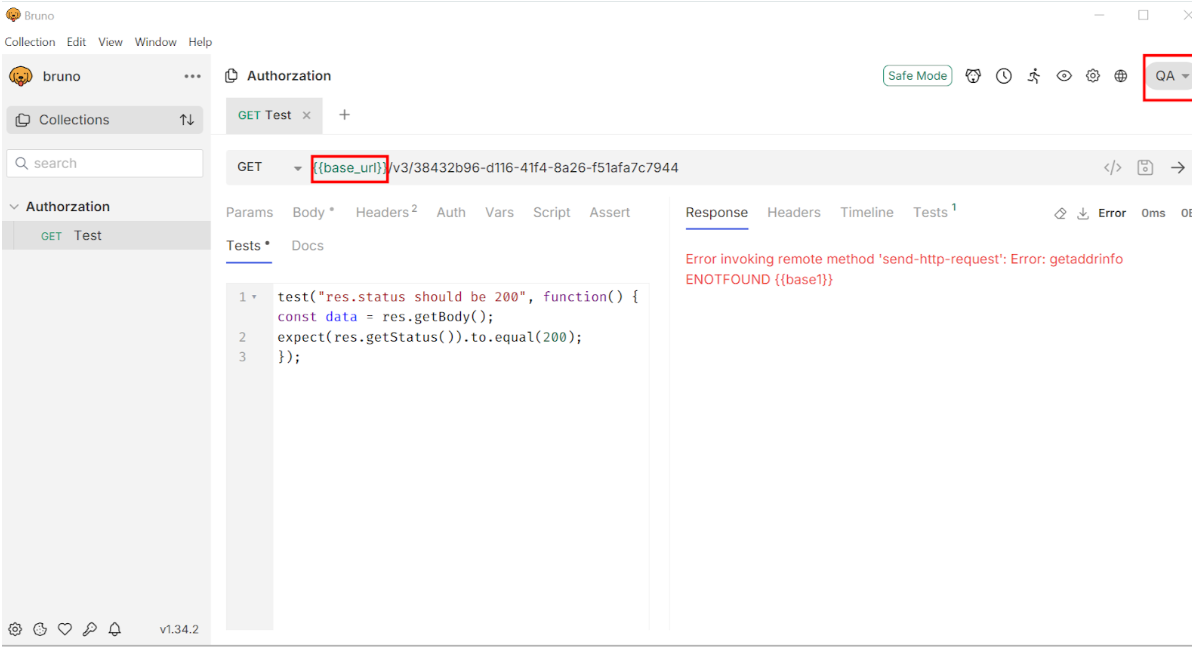
Step 10: Environment Variables (Optional)
Set up environment variables to manage variables like API keys, tokens, and URLs. This makes it easy to switch between environments (e.g., development, staging, production).
Bruno uses YAML for environment configurations, which you can structure as:
base_url: “https://api.example.com”
token: “your_access_token”
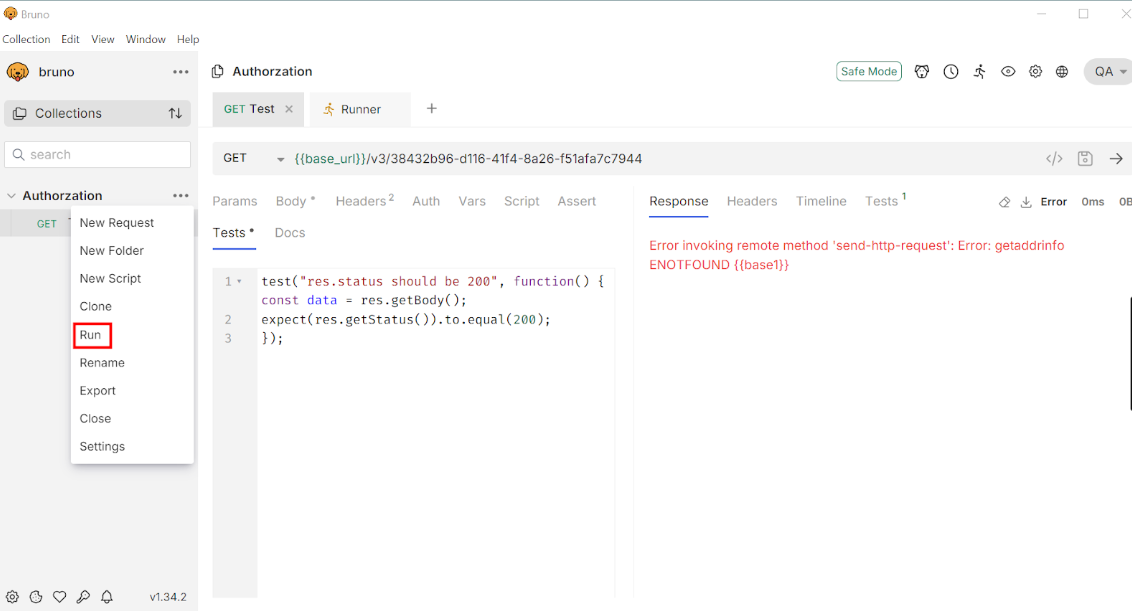
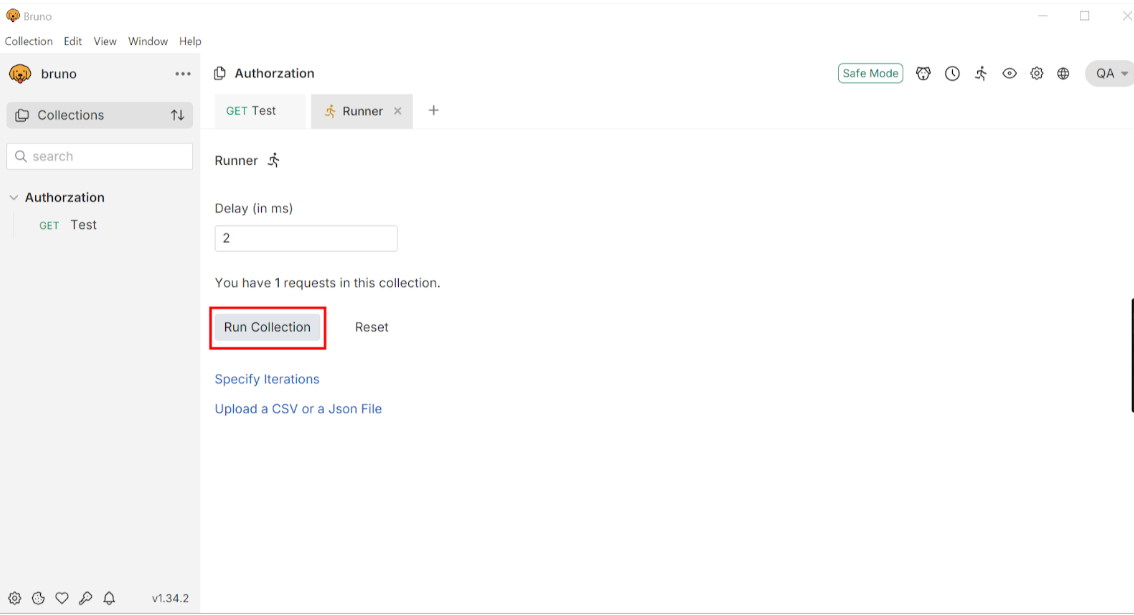
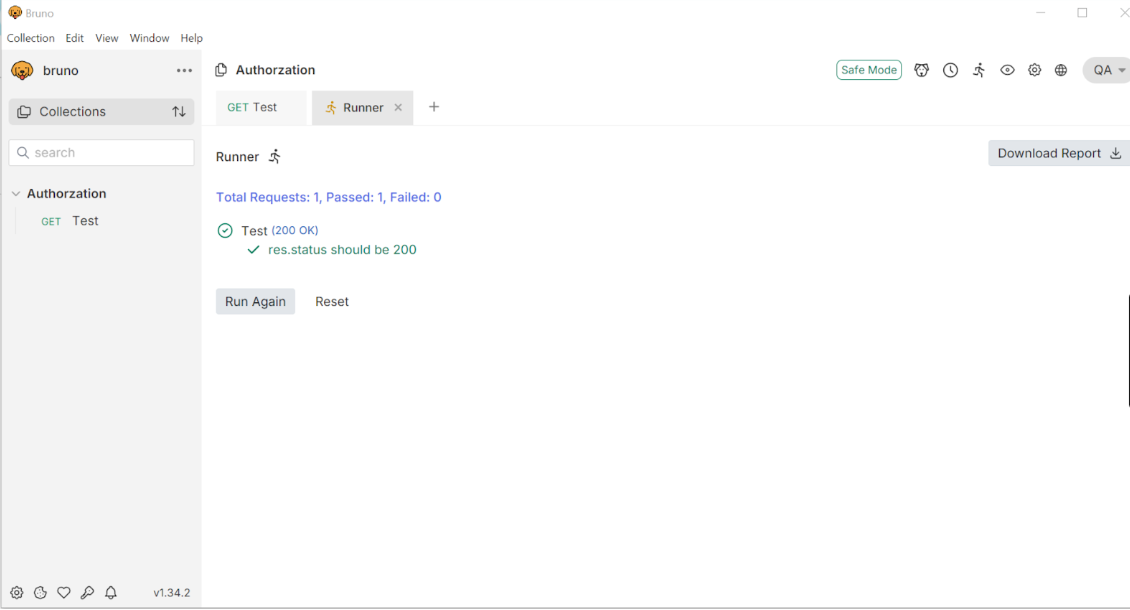
Step 11: Run Collection Tests (Optional)
For testing multiple endpoints in a sequence, run the entire collection. This helps with integration testing or verifying multiple API workflows.
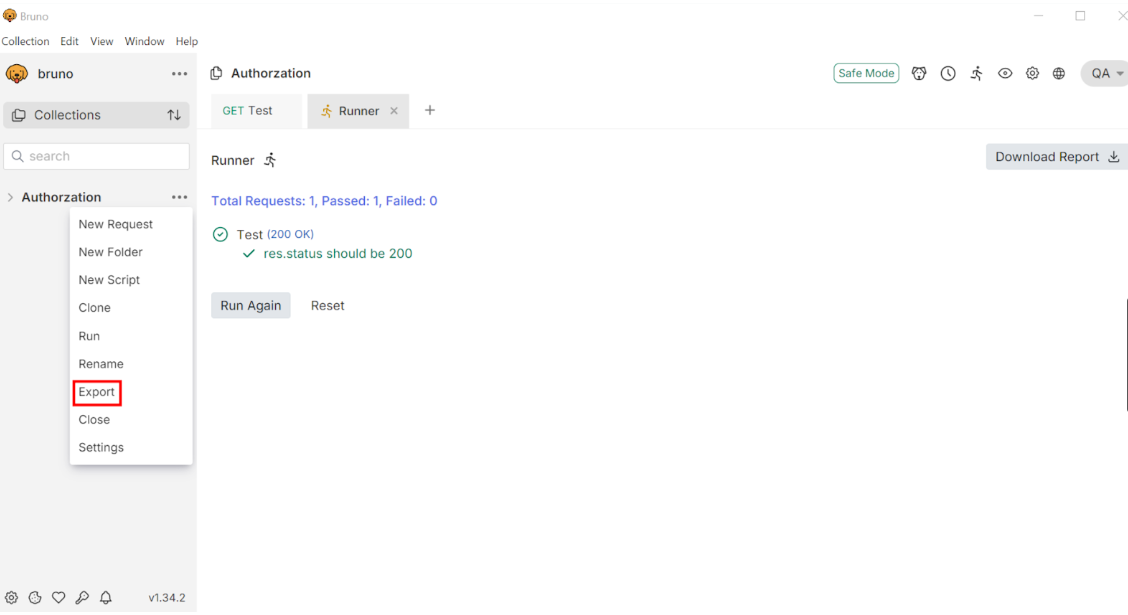
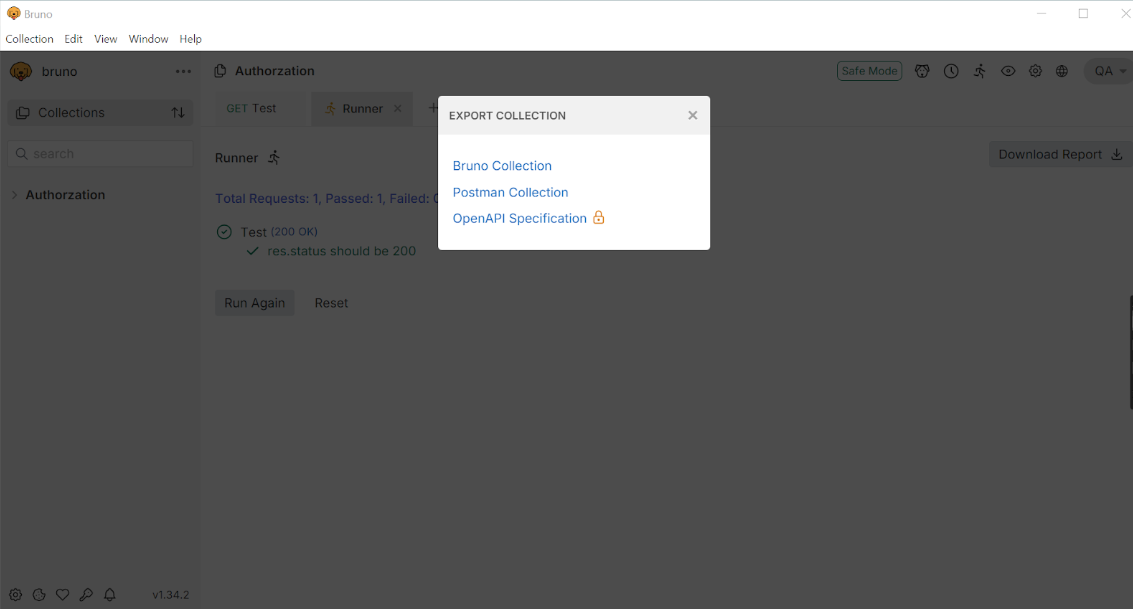
Step 12: Export and Share Collections
Export collections or share them with team members. This is useful for collaborative testing and documentation.
Step 13: Review Logs and Debugging
Check Bruno’s logs for detailed information about each request. This helps debug issues or refine requests if the API isn’t behaving as expected. In this Bruno tutorial, we show you how to effectively use the log feature for reviewing and debugging requests.
Security and Secret Management in Bruno
Bruno provides built-in support for handling sensitive API data securely.
Key security capabilities include:
Support for `.env` files to manage API keys and tokens
Secret variables to avoid exposing sensitive values
Automatic masking of tokens and credentials in reports
These features help teams securely manage API testing workflows without exposing confidential data.
Bruno in Modern API Testing
Modern applications increasingly rely on APIs, making API-first testing more important than ever.
Bruno fits well into modern testing workflows with:
Lightweight architecture
Git-based collaboration
Local API collection storage
CI/CD-friendly workflows
This makes Bruno a strong choice for teams adopting modern API testing practices.
Conclusion
In conclusion, learning API testing with Bruno can make testing easier. If you understand the basics and start using Bruno, it can change your testing approach. Bruno has a simple design and several features that set it apart from other tools. Whether you are new or experienced, Bruno makes API testing easy to use. You can see how Bruno works well with CI/CD pipelines and different API requests. Boost your testing with Bruno, the tool that simplifies your API testing tasks. For more detailed guidance, check out this Bruno tutorial to help you get started and master the platform..
Want to build secure, Git-friendly API testing workflows with Bruno?
What Makes Bruno Different from Other API Testing Tools?
Bruno operates completely offline. This is different from cloud-based options. By doing this, it keeps your data safe without using outside servers. You can import files from Postman and Insomnia. However, Bruno does not support cloud syncing. This is why it is a secure choice for projects that need extra protection.
How Do I Migrate My Existing Postman Tests to Bruno?
Bruno helps you move your data easily. You can import collections from Postman and Insomnia right away. Just go to the Import Collection feature and select your Postman or Insomnia file. Bruno handles the API request scripts to make the process smooth.
Can Bruno Be Integrated with CI/CD Pipelines?
Bruno is great at CI/CD workflows. You can use its command-line interface easily. Just type the bru run command in your pipeline scripts. This will help you start testing and include complete API testing in your automated tasks.
What Types of API Requests Can Bruno Handle?
Bruno supports several types of API requests. These are GET, POST, PUT, DELETE, PATCH, and more. This flexibility makes Bruno useful for testing RESTful APIs, GraphQL, and other types of API structures.
Where Can I Find More Resources on Using Bruno for API Testing?
For more information, tutorials, and community help, visit the official Bruno documentation on their website. You can also check out the Bruno repository on GitHub. These resources provide useful insights and tips to get the best from Bruno.
In today’s quick software development world, it is important to keep apps high quality. A key part of this is software testing. Tosca automation is a strong tool that helps with this task. This blog, titled “Tosca Automation Tutorial: Model-Based Approach,” will cover the main points about Tosca. We will look into its new model-based method to make your software testing better.
Key Highlights
Learn how Tricentis Tosca can make your software testing process easier.
This blog gives a simple look at Tosca, its features, and how it helps with test automation.
Find out how Tosca’s model-based approach allows you to create tests quickly, reuse them often, and ease maintenance.
We will explore real-world examples of how Tosca works well in different environments.
If you are new to Tosca or want to enhance your automation skills, this guide has helpful tips for using Tosca in your testing tasks.
Exploring the Core of Tosca Automation
Tosca automation, from Tricentis, is a top test automation tool. It helps make software testing easier and faster. Its simple design and strong features let you create, manage, and run automated tests easily. This means less manual work and faster software delivery.
Tosca is special because it uses a model-based approach. This means it creates reusable test pieces for the application being tested. Tosca simplifies technical details. As a result, both technical and non-technical people can join in test automation.
Unveiling the Features of Tosca Automation
Tosca is a powerful tool that makes testing easy and quick. One great feature of Tosca is how simple it is to create test cases. Users can use a drag-and-drop design to build their test cases. They do not need to know a lot about coding to do this.
Tosca offers excellent test data management. The platform helps you handle test data easily. This way, tests are completed with the right inputs and checks. A straightforward method to manage data cuts down on mistakes and makes test results more reliable.
Tosca is not just about basic needs. It offers many advanced features. These features include risk-based testing and API testing. Also, it connects easily with CI/CD pipelines. This makes it a great choice for software development today.
How Tosca Stands Out in the Automation Landscape
Tosca test automation stands out from other automation tools. It has special features that fit the needs of software testing. It is easy to use. Even those with little technical skills can use it without any trouble.
Tosca is not only about running tests. It covers the whole testing process. It works well with popular development and testing tools. This makes it easy for teams to add Tosca to what they already do. They can then work better together and get feedback faster.
Tosca works with many platforms and technologies. It can do several testing tasks. You can test web applications, mobile apps, APIs, or desktop applications using it. Tosca offers the flexibility and power you need to cover all tests completely.
What is Model-Based Approach?
The model-based approach changes how we make and manage test cases. It is different from the old script-based method. The traditional way takes a lot of time and is hard to keep up to date. Model-based testing focuses on creating a model of the application we are testing. This model is important because it illustrates how the app works. It includes details about its features, buttons, and logic.
With this method, the design of tests is separate from the code. This makes it easy to reuse tests and manage them. When the application is updated, testers only need to change the main model. These changes will then automatically update all connected test cases. This is very useful for keeping test suites current with changing applications. Therefore, it works well for quick development, especially in the functional testing of web applications.
Uniqueness of model-based approach
Model-based testing is important because it can change with the application. Rather than depending on weak scripts that may fail with each update, the model serves as a guide. This flexible approach helps keep tests helpful and efficient, even as software keeps changing.
This method is easy to understand. Testers can clearly see how the application works and what the test scenarios look like with the model. This visual approach supports teamwork between testers and developers. Both sides can understand and help with the testing process.
Enhance Reusability
At the core of model-based testing is reusable test libraries. These libraries keep parts of tests that you can use again. They include common actions, checks, and business tasks. When testers create a library of these reusable pieces, they can save a lot of time and effort. This helps them make new test cases much easier.
This method helps keep practice steady. When teams use ready-made and tested modules, they make fewer mistakes. They also stick to software processes.
We enjoy many benefits. These include better test coverage, faster test execution, and improved software quality. When companies use reusable test libraries, they can enhance their testing process. This helps them create great software that meets high standards.
Responsive Object Recognition
Tosca automation uses smart object recognition. This feature makes it different from regular testing tools. It allows Tosca to interact with application interfaces the same way a person would.
Tosca’s object recognition is more than just spotting items based on their features. It uses smart algorithms to learn the context and connections between different parts of the user interface. This helps Tosca deal with challenging situations in a better way.
Tosca is a good choice for testing apps that change regularly or need updates often. This includes testing for web, mobile, and desktop applications.
Reusable Test Libraries and Steps
Reusable test libraries are key for Tosca’s model-based method. They help testers build test parts that are simple to join and use. This speeds up the test creation process. It also supports best practices in testing.
Testers can make and save test steps in these libraries. A test step means any action or engagement with the application they are testing. Some test steps can be simple, like clicking a button. Others can be more complicated, like filling out forms or moving through different screens.
By putting these common test steps in reusable libraries, Tosca helps teams create a strong test automation framework. This way, it cuts down on repeated tasks and makes maintenance simpler. It also ensures that tests remain consistent and trustworthy.
Streamlined Testing and Validation
Tosca’s method makes testing simpler and well-organized. It keeps the test logic apart from the code. This setup helps teams build and run tests more quickly. Because of this, they get feedback fast. It helps them spot and solve issues early in the software development process.
Finding problems early is key to keeping high quality in software development. With Tosca, testers can make test suites that look at many different scenarios. This way, applications can be tested thoroughly before they go live. It helps lower the number of costly bugs and problems in production.
When companies use Tosca’s easy testing and checking methods, they can make their software better. This saves them time when they launch their products. A better software position means they can provide great user experiences. It also helps them stay on top in today’s fast software world.
Step-by-Step Guide to Implementing Model-Based Approach in Tosca
Step 1: Understand Model-Based Approach in Tosca
Learn about Tosca’s approach to model-based testing. It focuses on making and reusing models of the application. This way makes it easier to create and keep test cases.
Benefits:
Broad Scenario Testing: Model based testing allows testing a wide range of scenarios without embedding logic or data into the test cases directly.
Code-Free Models: Models are visual, code-free, and highly reusable, making MBT accessible to non-developers.
Ease of Maintenance: Updating a single model or data set propagates to all tests relying on it, reducing maintenance time.
Step 2: Set Up Your Tosca Environment
Install Tosca: Ensure you have the latest version of Tricentis Tosca installed.
Download and Install: Visit Tricentis to download Tosca. Run the installer, accept terms, select components (like Tosca Commander), and complete the setup.
Chrome Extension: For web automation, add the “Tosca Automation Extension” from the Chrome Web Store.
Initial Setup: Launch Tosca, activate your license, and set up a new project workspace. Create folders for Modules, Test Cases, and Execution Lists.
Click > create new
In the subsequent Tosca Commander: Create new workspace window, select Oracle, MS SQL Server, or DB2 from the Select type of Repository drop-down menu.
Click OK to create a new workspace
To view the project structure, click on the Project
Configure Project Settings: Set up your workspace. Also, adjust any necessary settings for your project in Tosca, such as database or API connections.
Step 3: Create the Application Model
Find and Scan Your Application (AUT):
1.Open the Scanner: Tosca has different scanning options based on the application type (web, desktop, or mobile). Launch the scanner through Tosca Commander > Scan Application.
2.Identify Controls: For a web app, for example, open the browser and navigate to the AUT. Select the web scanner, and Tosca will display elements (buttons, input fields, etc.) as you hover over them.
Right click on Modules > scan > Application
3.Select and Capture: Click to capture relevant elements for testing. Tosca will record these elements in a structured format, enabling them for reuse in different test cases.
Create Modules: Organize these parts into modules. These modules are the foundation for your test cases.
Modules: Reusable components in Tosca for parts of an application (e.g., login screen with fields and buttons).
Sub-Modules: Smaller sections within a Module, used for complex screens with multiple sections (e.g., product details in an e-commerce app).
To create a sub-module (Right click on the module > create folder
Step 4: Design Test Cases Using the Model
Define Test Steps: Drag and Drop Elements: In Tosca Commander, start a new test case and drag elements from modules to create test steps. Arrange these steps in the order users typically interact with the application (e.g., navigating to login, entering credentials, and submitting).
Specify Actions and Values: For each step, specify actions (click, input text) and values (e.g., “username123” for a login field).
Input (Standard): Enters values into test objects (e.g., text fields, dropdowns). Verify: Checks if test object values match expected results. Buffer: Captures and stores data from test objects for later use. WaitOn: Pauses execution until a specific condition is met on a test object. Constraint: Defines conditions for filtering or selecting rows in tables. Select: Selects items or rows in lists, grids, or tables based on criteria.
Parameterize Test Steps: Include parameters to make tests flexible and based on data. This helps you run tests with various inputs.
Step 1: Create a Test Sheet in Test Case Design
Go to the Test Case Design section in Tosca.
Create a New Test Sheet: Right-click on the Test Case Design folder and select
Create Test Sheet Name your test sheet, e.g., “Environment Test Data.”
Add Test Cases/Parameters to the Test Sheet:
Add rows for the different environments (QA, Prod, and Test) with their respective values.
1.Right click on the sheet > Create Instance
2.Create your own instance e.g., “QA, PROD”
3.Double-click on the sheet for a more detailed instance view.
4.Right click on the sheet > Create Attribute
5.Inside the attribute, add parameters (e.g., URL, Username, Password).
6.For single attributes, we can add multiple instance values [Right click on the attribute > click create instance]
7.We can create a multiple instance (Test data) for single attribute
8.And select user 1 or user 2 according to you test case from drop-down Note: Newly added instance will be displayed under the attribute drop-down
Step 2: Create Buffers and Link to Test Case
Create Test Case: Open Tosca, right-click the desired folder, choose Create Test Case, and name it has “Buffer”.
Add Set Buffer Module: In Modules, locate Standard modules >TBox Automation Tools>Buffer Operations>TBox Set Buffer and drag it into the test case.
Convert Test Case to Template: Right-click on the test case, select Convert to Template. This action makes the test case reusable with different data.
Drag and drop, to map the test sheet from Test Case Design to the Test Case Template
After mapping the test sheet to the template test case, you can assign the test sheet attributes to buffer values for reuse within the test steps
Now, you can generate template instances for the created instance, Right-click on the Template Test Case and click > Create TemplateInstance.
Tosca will create separate instances under the template test case, each instance populated with data from one row in the test sheet.
Step 3: Run the Test Case and View Buffer Values in Tosca
Run the test case and view buffer values in Tosca:
Navigate to the Template Test Case Instances:
-Go to Test Cases in Tosca and locate the instances generated from your template test case.
Run the Test Case:
-Right-click on an instance (or the template test case itself) and select Run.
-Tosca will execute the test case using the data from the test sheet, which has been mapped to buffers.
Check the Execution Log:
-After execution completes, right-click on the instance or test case and select Execution Log.
-In the Execution Log, you’ll see detailed results for each test step. This allows you to confirm that the correct buffer values were applied during each step.
Open the Buffer Viewer:
-To further inspect the buffer values, open the Buffer Viewer:
-Go to Tools > Buffer (or click on the Buffer Viewer icon in the toolbar).
-The Buffer Viewer will display all buffer values currently stored for the test case, including the values populated from the test sheet.
Verify Buffer Values in Buffer Viewer:
-In the Buffer Viewer, locate and confirm the buffer names (e.g., URL_Buffer, Username_Buffer) and their corresponding values. These should match the values from the test sheet for the executed instance.
-Verify that each buffer holds the correct data based on the test sheet row for the selected instance (e.g., QA, Prod, Test environment data).
Re-run as Needed:
-If needed, you can re-run other instances to verify that different buffer values are correctly populated for each environment or row.
Step 4: Using Buffers in Test Cases
In any test step where you want to use a buffered value, type {B[BufferName]} (replace BufferName with the actual name of your buffer).
For example, if you created a buffer called URL, use {B[URL]} in the relevant test step field to retrieve the buffered URL.
Step 5: Build Reusable Libraries and Test Step Blocks
Create Libraries: Build libraries or testing steps that can be reused. This saves time and reduces work that needs to be done repeatedly.
Divide and Organize: Arrange reusable sections so you can use them in various test cases and projects.
Step 6: Execute Test Cases
In Tosca, test cases can be executed in two main ways:
Feature
Scratchbook
Execution List
Purpose
For ad-hoc or quick test runs during development and troubleshooting.
Designed for formal, repeatable test runs as part of a structured suite.
Persistence of Results
Temporary results; they are discarded once you close Tosca or re-run the test case.
Persistent results; saved to Tosca’s repository for historical tracking, reporting, and analysis.
Control Over Execution
Limited configuration; runs straightforwardly without detailed settings.
Detailed execution properties, including priorities, data-driven settings, and environment configurations.
Suitability for CI/CD
Not intended for CI/CD pipelines or automated execution schedules.
Commonly used in CI/CD environments for systematic, automated testing as part of build pipelines.
Scheduling & Reusability
Suitable for one-off runs; not reusable for scheduled or repeatable tests.
Can be scheduled and reused across test cycles, providing consistency and repeatability.
Steps to Execute TestCases in Scratchbook
Select TestCases/TestSteps in Tosca’s TestCases section.
Right-click and choose Run in Scratchbook.
View Results directly in Scratchbook (pass/fail status and logs).
Steps to Set Up an Execution List in Tosca
Identify the TestCases: Determine the test cases that need to be included based on the testing scope (e.g., manual, automated, API, or UI tests).
Organize Test Cases in the Test Case Folder: Ensure all required test cases are organized within appropriate folders in the Test Cases section.
Create an Execution List:
-Go to the Execution section of Tosca.
-Right-click > Create Execution List. Name the list based on your testing context (e.g., “Smoke Suite” or “Regression Suite”).
Drag and Drop Test Cases:
-Navigate back to the TestCases section.
-Drag and drop the test cases (or entire test case folders if you want to include multiple tests) into your execution list in the Execution section.
–Save and Execute: Save the execution list, then execute it by right-clicking and selecting Run.
-The execution will start, and progress is shown in real-time.
– After execution, you can view the pass/fail status and logs in Execution Results
Navigate to Execution Results:
-Navigate back to the TestCases section.
-You’ll see each TestCase with a pass (green) or fail (red) status.
Step 7: Review and Validate Test Results
Generate Reports:
-After execution, go to Execution Results.
-Right-click to print reports in various formats (Excel, PDF, HTML, etc.) based on your requirements.
Choose Export Format:
-Select the desired format for the export. Common formats include:
-Excel (XLSX)
-PDF
-HTML
-XML
-After exporting your execution results to a PDF in Tosca, you can view the PDF
Check Results: Use Tosca’s reporting tools to look at the test execution results. See if there are any issues.
Record and Document Findings: Write down everything you find. This includes whether the tests pass or fail and any error details.
Step 8: Maintain and Update Models and Test Cases
Get used to changes: Update your sections and test cases as your application grows. Make changes directly in the model.
Make it easy to reuse: Keep improving your parts and libraries. This will help them remain usable and function well.
Benefits of using the Model-Based Approach in Tosca Automation
The benefits of using Tosca’s model-based approach are many. First, it greatly speeds up test automation. A major reason for this is reusability. When you create a module, you can use it for several test cases. This saves time and effort when making tests.
One big benefit is better software quality. A model-based approach helps teams build stronger and more complete Tosca test suites. The model provides a clear source of information. This allows the test cases to show how the application works correctly. It also helps find mistakes that may be missed otherwise.
Comparison of the Model-Based Approach with traditional methods of Tosca Automation
When you look at the model-based approach and compare it to the old Tosca automation methods, the benefits are clear. Traditional testing requires scripts. This means it takes a long time to create test suites. It is also hard to maintain them. As applications become more complex, this problem gets worse.
The model-based approach helps teams be flexible and quick. It allows them to adapt to changes smoothly. This is key for keeping up with the fast pace of software development. The back-and-forth process works well with modern development methods like Agile and DevOps.
Real-world examples of successful implementation of the Model-Based Approach in Tosca Automation
Many companies from different industries have had great success with Tosca’s model-based approach for automation. These real examples show the true benefits of this method in different environments and various applications.
Industry
Organization
Benefits
Finance
Leading Investment Bank
Reduced testing time by 50%, Improved defect detection rates
Healthcare
Global Healthcare Provider
Accelerated time-to-market for critical healthcare applications
Retail
E-commerce Giant
Enhanced online shopping experience with improved application stability
Conclusion
In conclusion, using the Model-Based Approach in Tosca Automation can really help with your testing. This method makes it easier to find objects and allows you to create reusable test libraries. With this approach, you will check your work and test more effectively. Following this method can lead to better efficiency and higher productivity in automation. Model-based testing with Tosca helps you design and run tests in a smart way. By trying this new approach, you can improve your automation skills and keep up in the fast-changing world of software testing. Companies like Codoid are continually innovating and delivering even better testing solutions, leveraging tools like Tosca to enhance automation efficiency and results. Check out the benefits and real examples to see what Tosca Automation offers with the Model-Based Approach.
Frequently Asked Questions
What Makes Tosca’s Model-Based Approach Unique?
Tricentis Tosca uses a model-based way to work. This helps teams get results quicker. It offers simple visual modeling. Test setup is easy and does not need scripts. Its powerful object recognition makes test automation easy. Because of this, anyone, whether they are technical or not, can use Tosca without problems.
How Does Tosca Automation Integrate with Agile and DevOps?
Tosca works well with agile and DevOps methods. It supports continuous testing and works nicely with popular CI/CD tools. This makes the software development process easier. It also helps teams get feedback faster.
Can Tosca Automation Support Continuous Testing?
Tosca Automation is an excellent software testing tool. It is designed for continuous testing. This tool allows tests to run automatically. It works perfectly with CI/CD pipelines. Additionally, it provides fast feedback for continuous integration.
What Resources Are Available for Tosca Automation Learners?
Tosca Automation learners can use many resources. These resources come from Tricentis Academy. You will find detailed documents, community forums, and webinars. This information supports Tosca test automation and shares best practices.